

Si deseas distinguir tus productos, servicios o ambos de los de otra empresa, es posible que necesites una marca o nombre comercial. Descubre qué son, en qué consiste su procedimiento de registro y qué implica.

Información sobre los plazos de presentación de solicitudes de transformación de marcas de la Unión Europea en marca nacional española. Más información


Si tienes un nuevo dispositivo, producto o procedimiento que resuelva un problema técnico o tenga una ventaja práctica, existen distintas formas de protegerlo en España y en otros países. Descubre cómo hacerlo.

¿Tu innovación reside en la estética, la ornamentación o la apariencia de tu producto? Protégela mediante un diseño industrial. Descubre qué derechos confiere el registro y cómo realizar la tramitación.

Las indicaciones geográficas protegen el nombre de un producto originario de una zona geográfica, a la cual le debe una determinada calidad, reputación u otra característica. Descubre qué son, en qué consiste su procedimiento de registro y qué beneficios conceden.

Las patentes publicadas en todo el mundo son una valiosa fuente de información científica, técnica y comercial.

Si eres emprendedor/a o una empresa y quieres potenciar y mejorar la rentabilidad de tu negocio protegiendo de forma adecuada los activos intangibles de tu organización, en este espacio encontrarás lo necesario.


 292
resultados
 Última actualización
24/10/2026 [09:06:00]


 Resultados 275 a 292 de 292
Resumen de: US20260222187A1
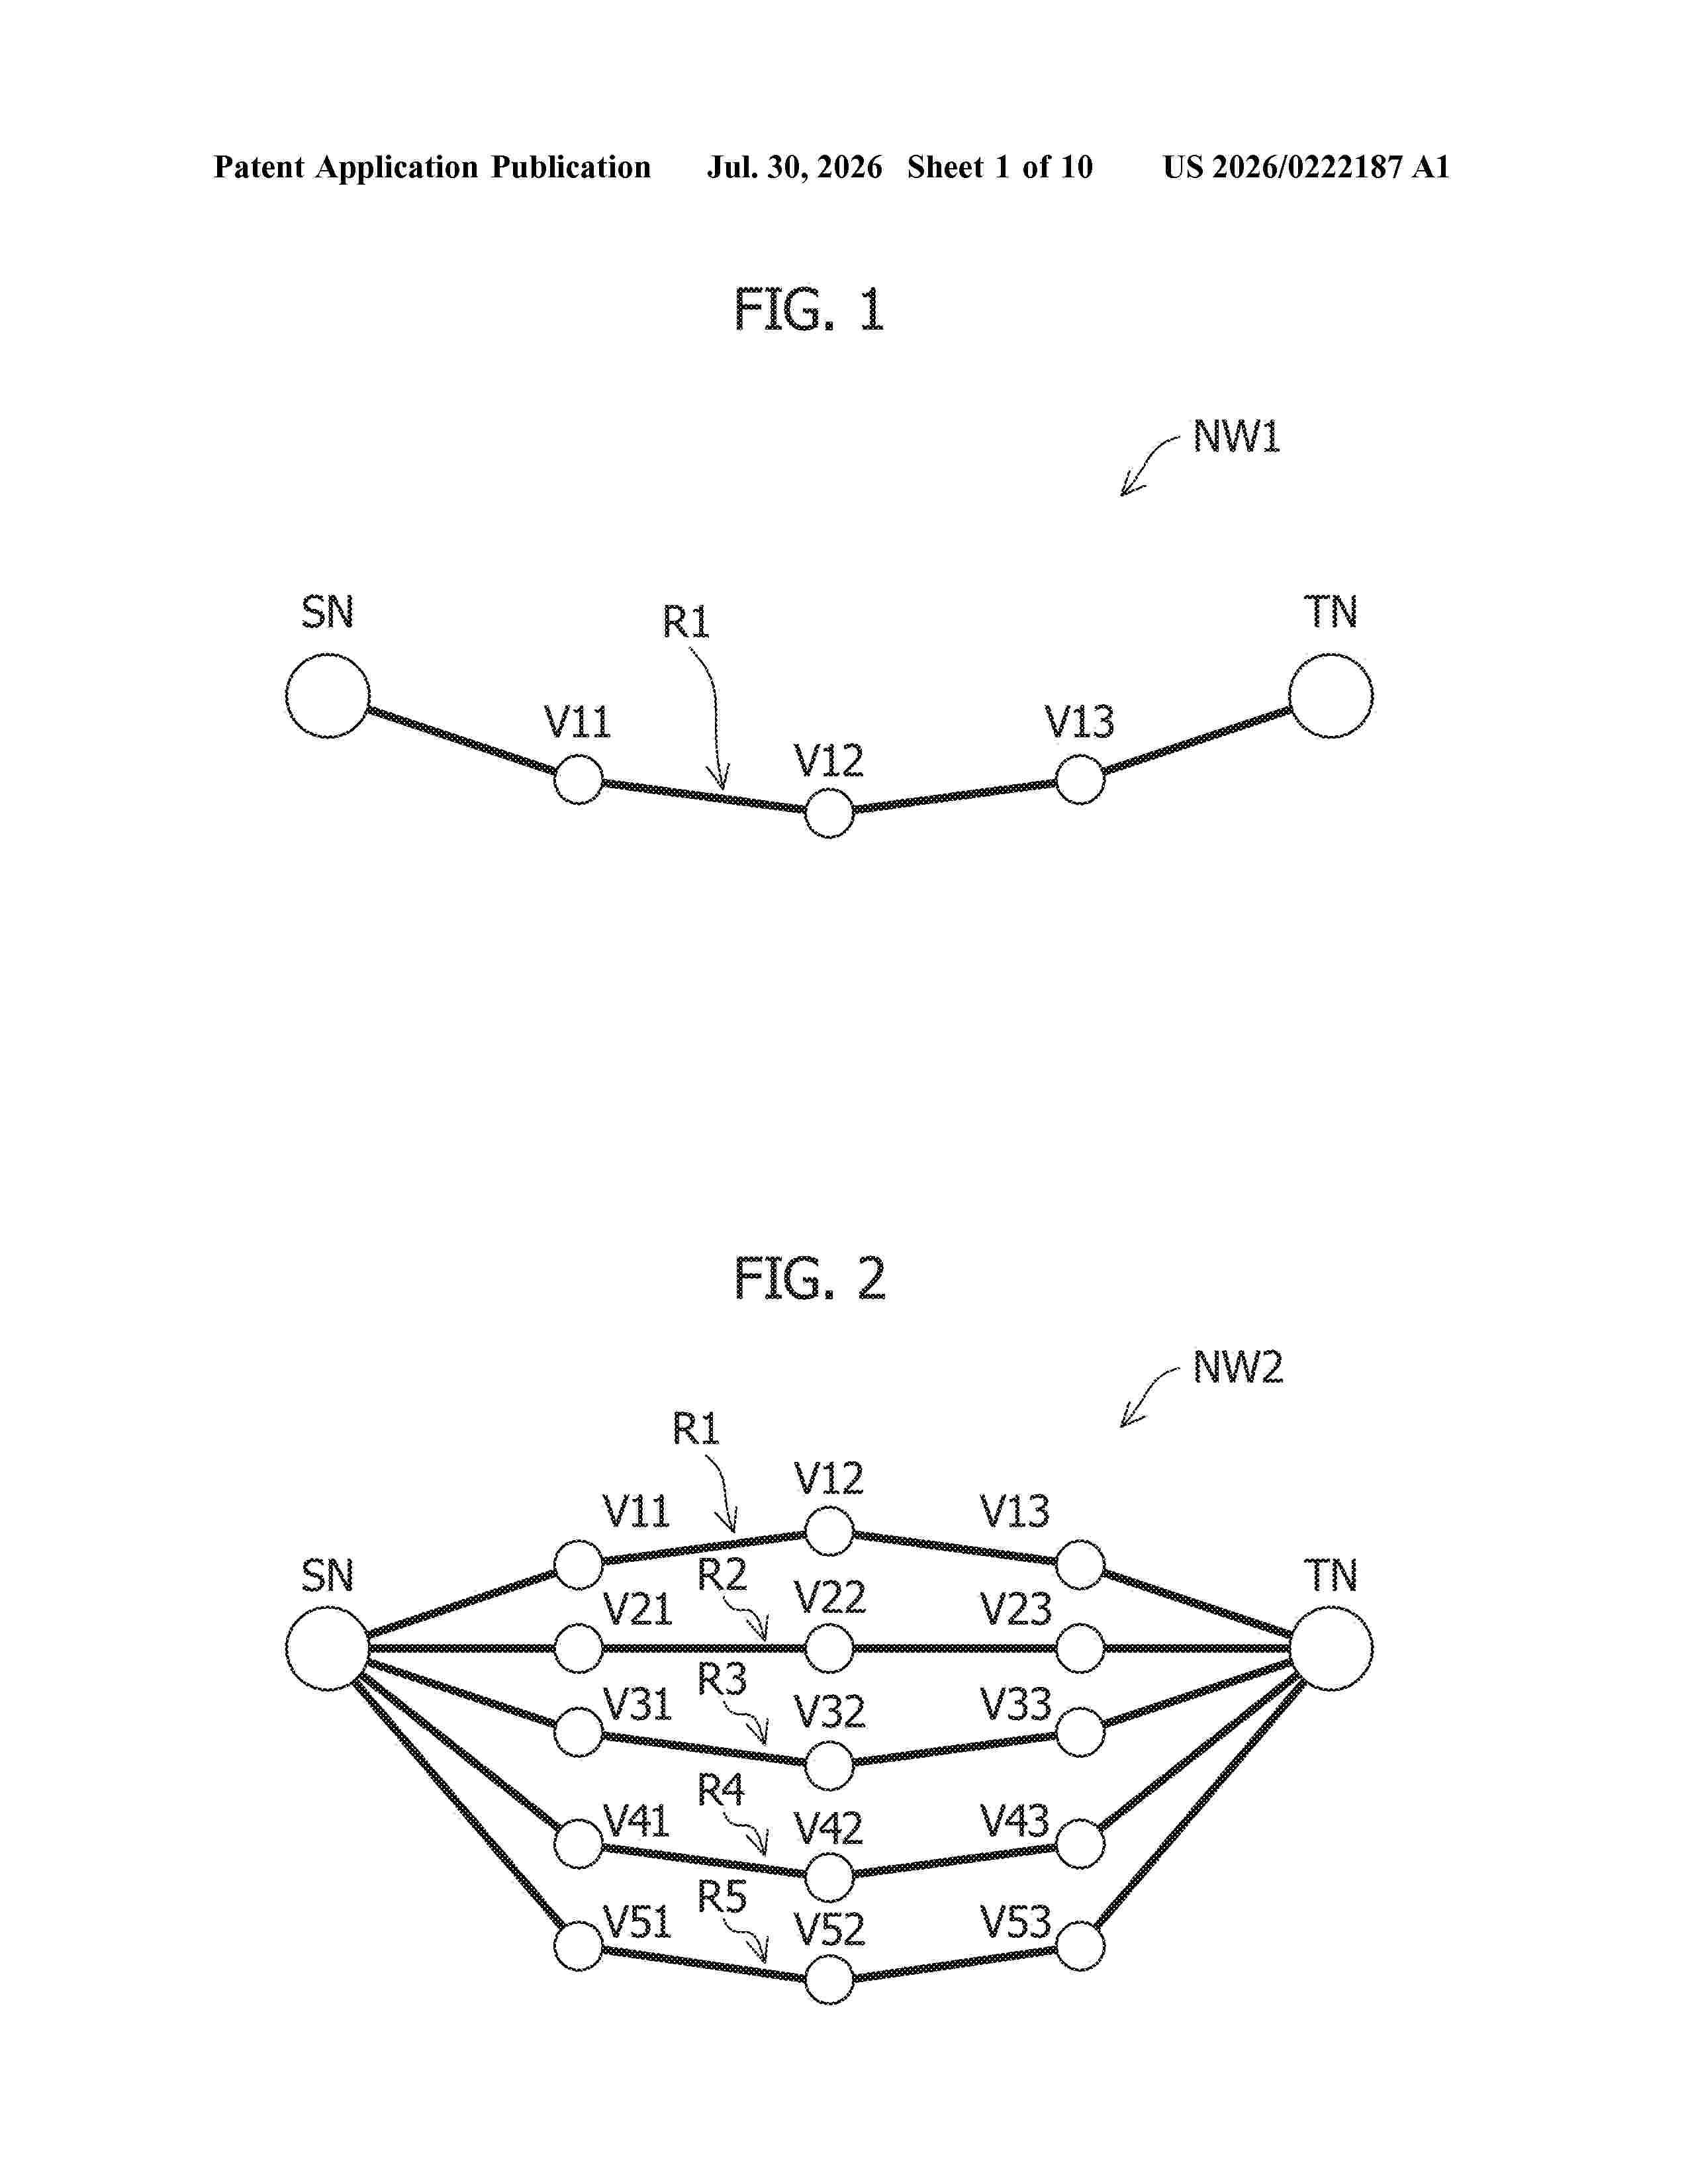
0000 The disclosed systems and methods assist transmitted content in reaching a receiver, even if a network is subjected to sophisticated tampering. A device for a communication network including a plurality of nodes and a plurality of paths connecting a source node, which is a transmission source of information, and a terminal node, which is a destination of the information. A segmentation instruction unit being configured to instruct the source node to disperse the information into a plurality of pieces of random number data, to encode the random number data by an error correction code to generate codewords, and to order the codewords from the beginning and divide the codewords into a plurality of segments, the first transmission instruction unit being configured to instruct the source node to transmit OTP-encrypted data of the plurality of segments through the plurality of paths.

Resumen de: WO2026160937A1
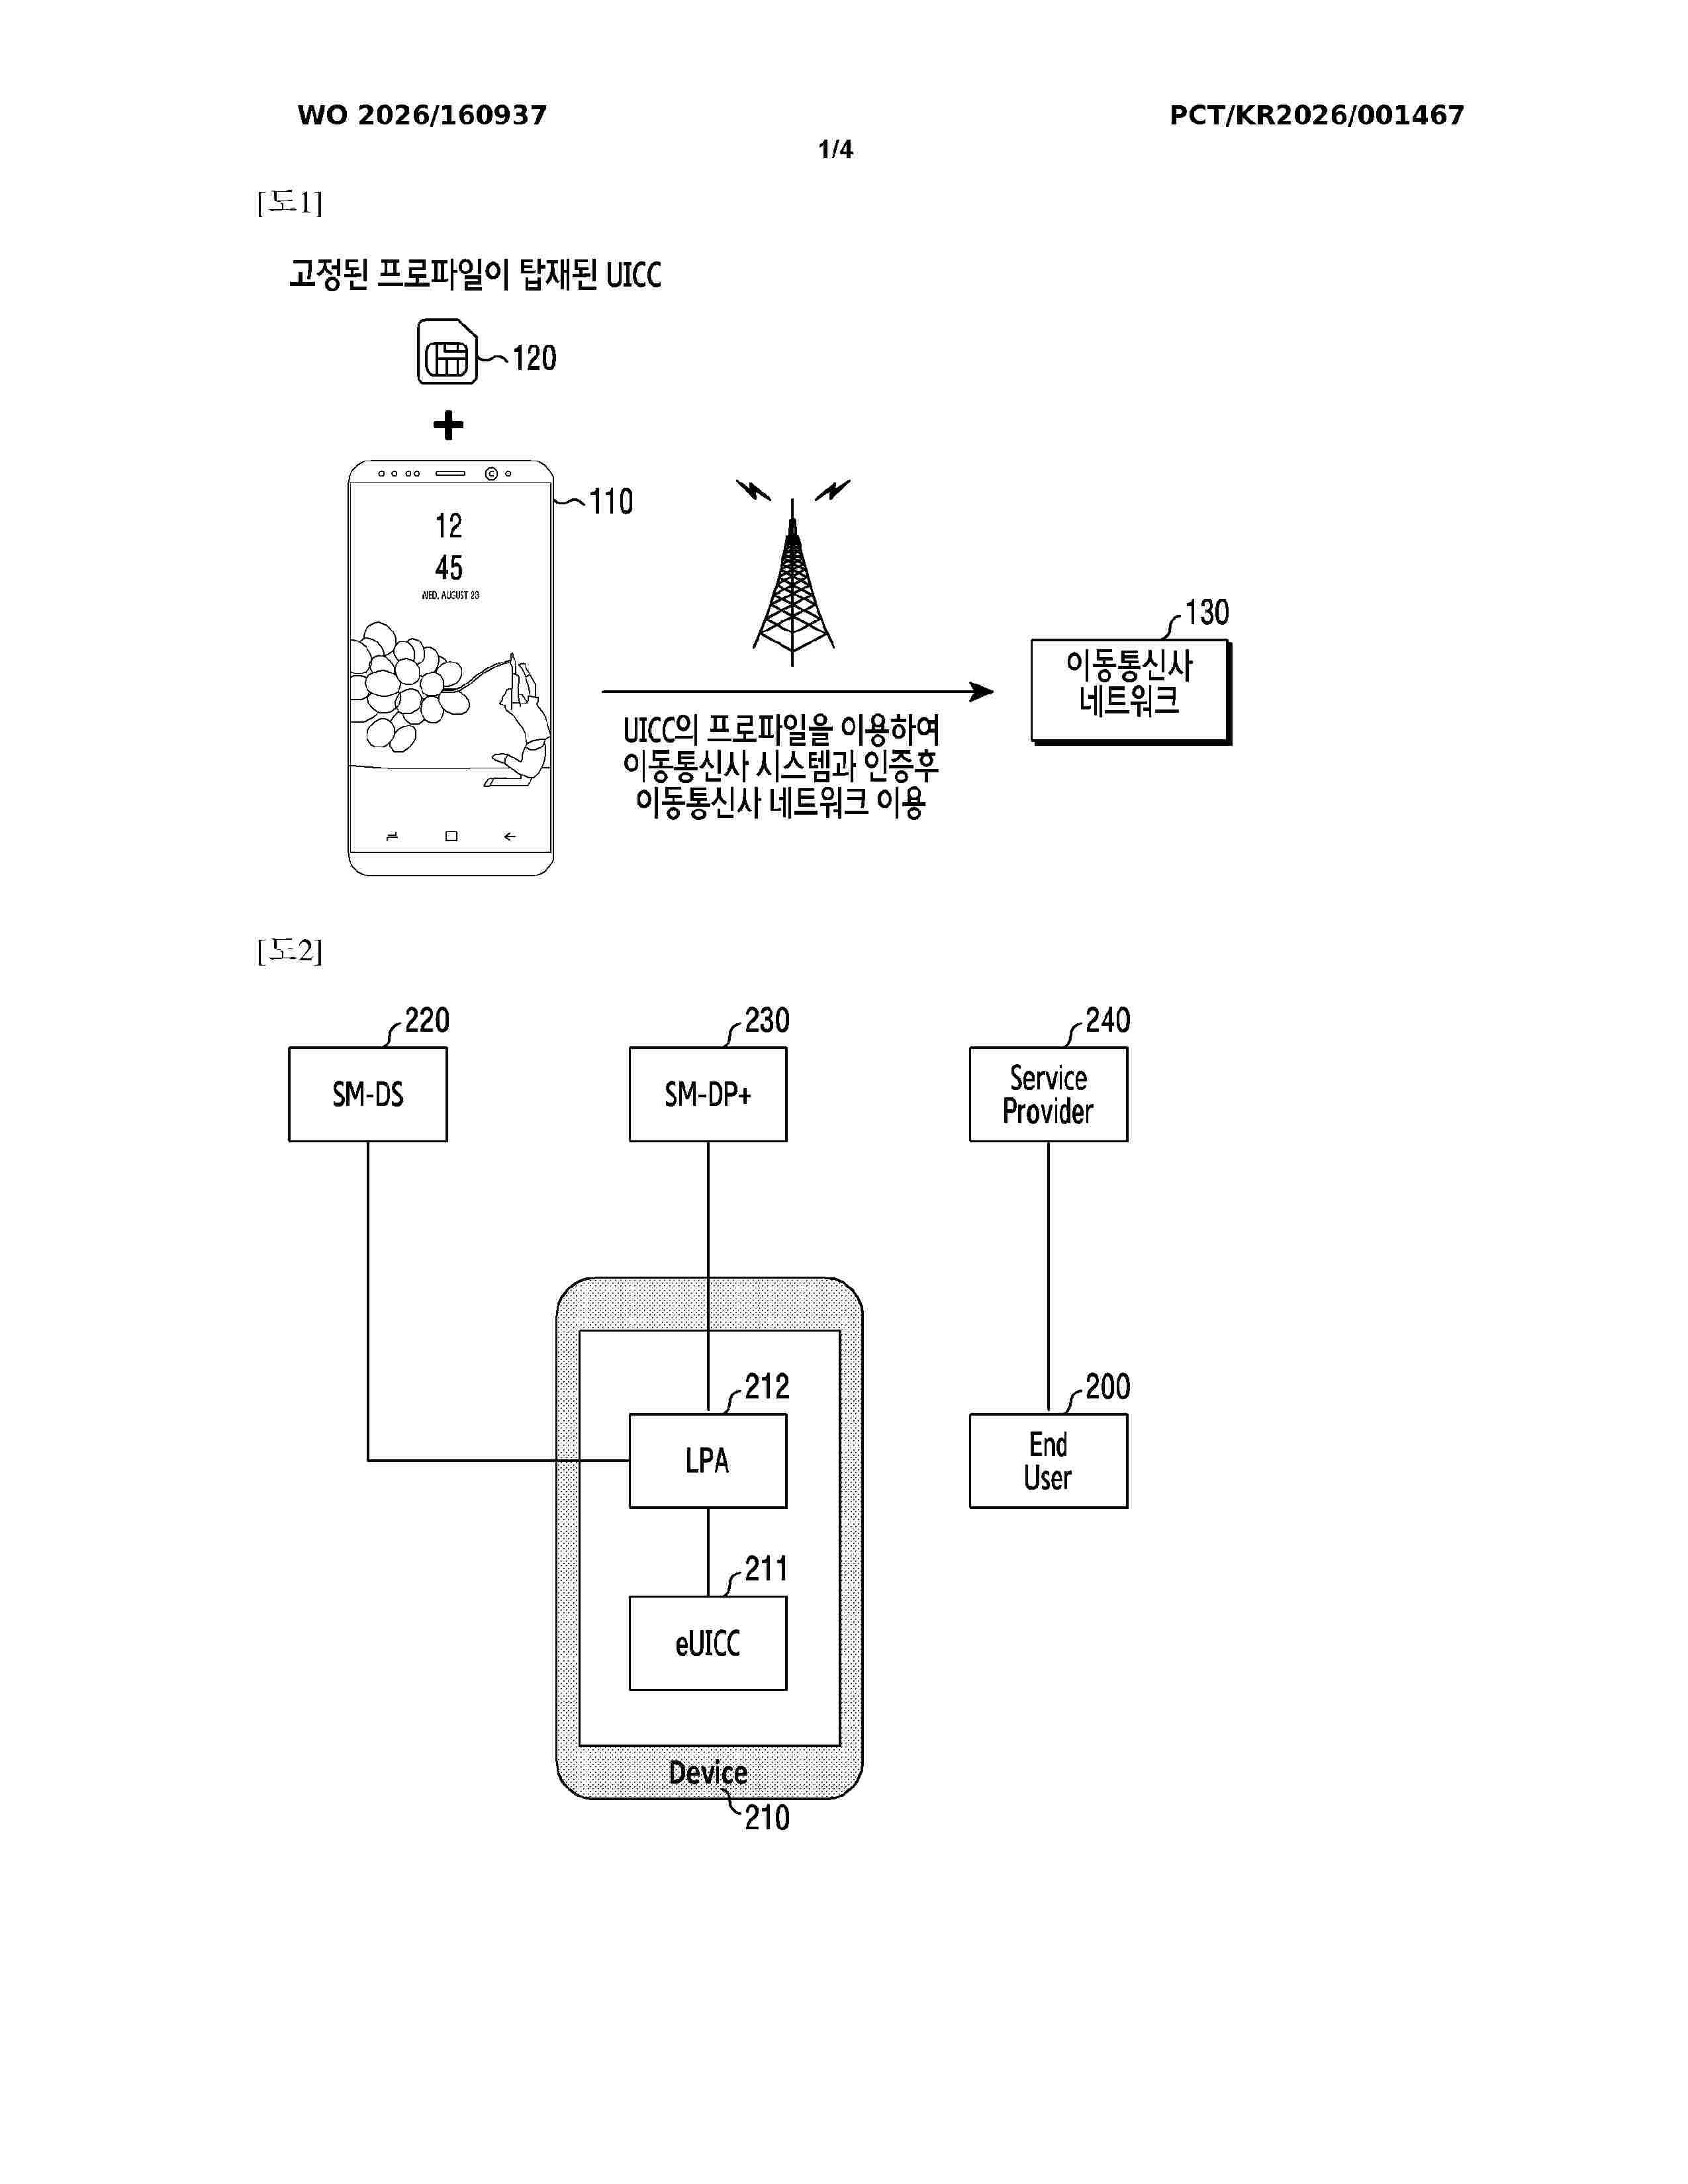
The present disclosure relates to a 5G or 6G communication system for supporting a higher data transmission rate. Provided is a method performed by a terminal of a wireless communication system. The method performed by a terminal according to an embodiment of the present disclosure may comprise the steps of: establishing a transport layer security (TLS) connection with a profile server; transmitting first embedded universal integrated circuit card (eUICC) information including first key configuration algorithm information supported by an eUICC of the terminal to the profile server through an authentication start request message for starting mutual authentication between the terminal and the profile server; receiving, from the profile server, an authentication start response message including information about at least one key configuration algorithm selected from the first key configuration algorithm information; transmitting, to the profile server through a client verification request message, an eUICC signature of the terminal and second eUICC information including second key configuration algorithm information supported by the eUICC of the terminal; and receiving, from the profile server, a response according to the verification result regarding whether the first key configuration algorithm information in the first eUICC information matches the second key configuration algorithm information in the second eUICC information.
Resumen de: US20260220242A1
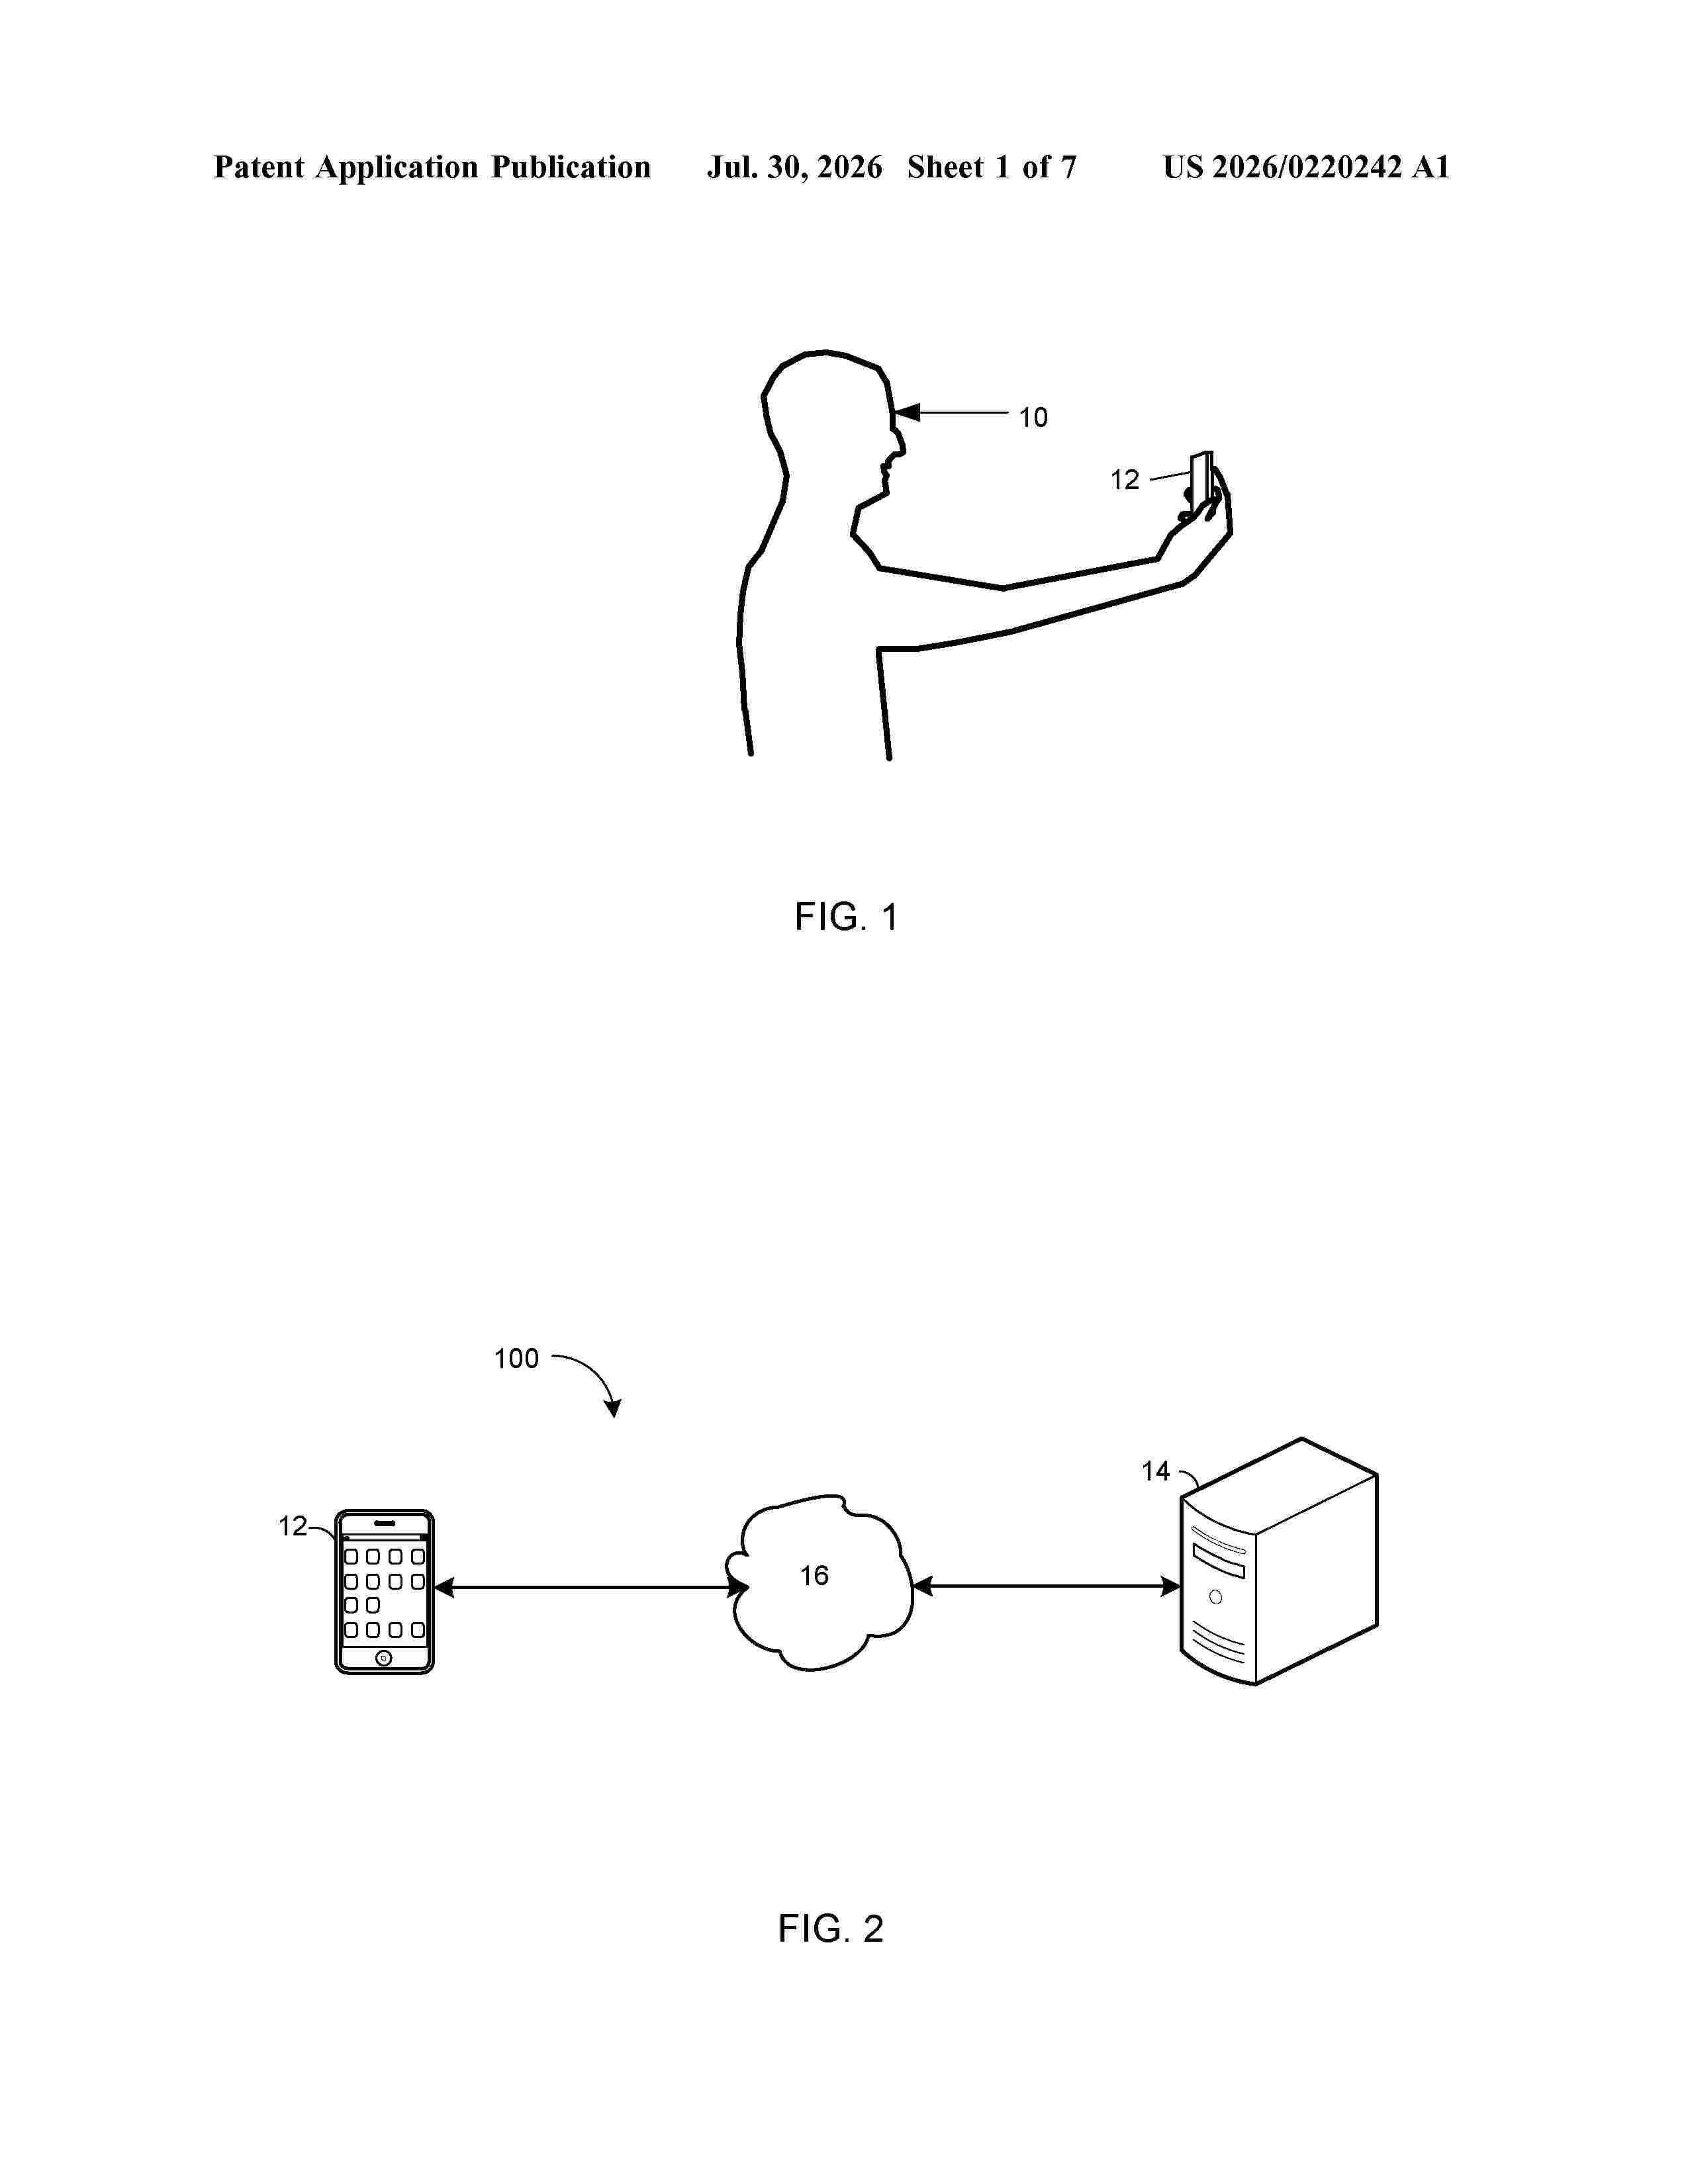
A method for enhancing detection of fraudulent authentication data includes receiving, by an electronic device, data during an authentication transaction, computing a feature vector from the received data, and normalizing the feature vector. The method also includes encoding the normalized feature vector into qubits, expanding, using at least one quantum algorithm, the normalized feature vector into a high-dimensional space, and detecting in the high-dimensional space anomalies indicative of fraud based on the qubits. Furthermore, the method includes calculating, based on the detected anomalies, a confidence score reflecting a likelihood that the received data is genuine and comparing the confidence score against a threshold value. In response to determining the confidence score fails to satisfy the threshold value, the method determines that the received data requires secondary authentication.
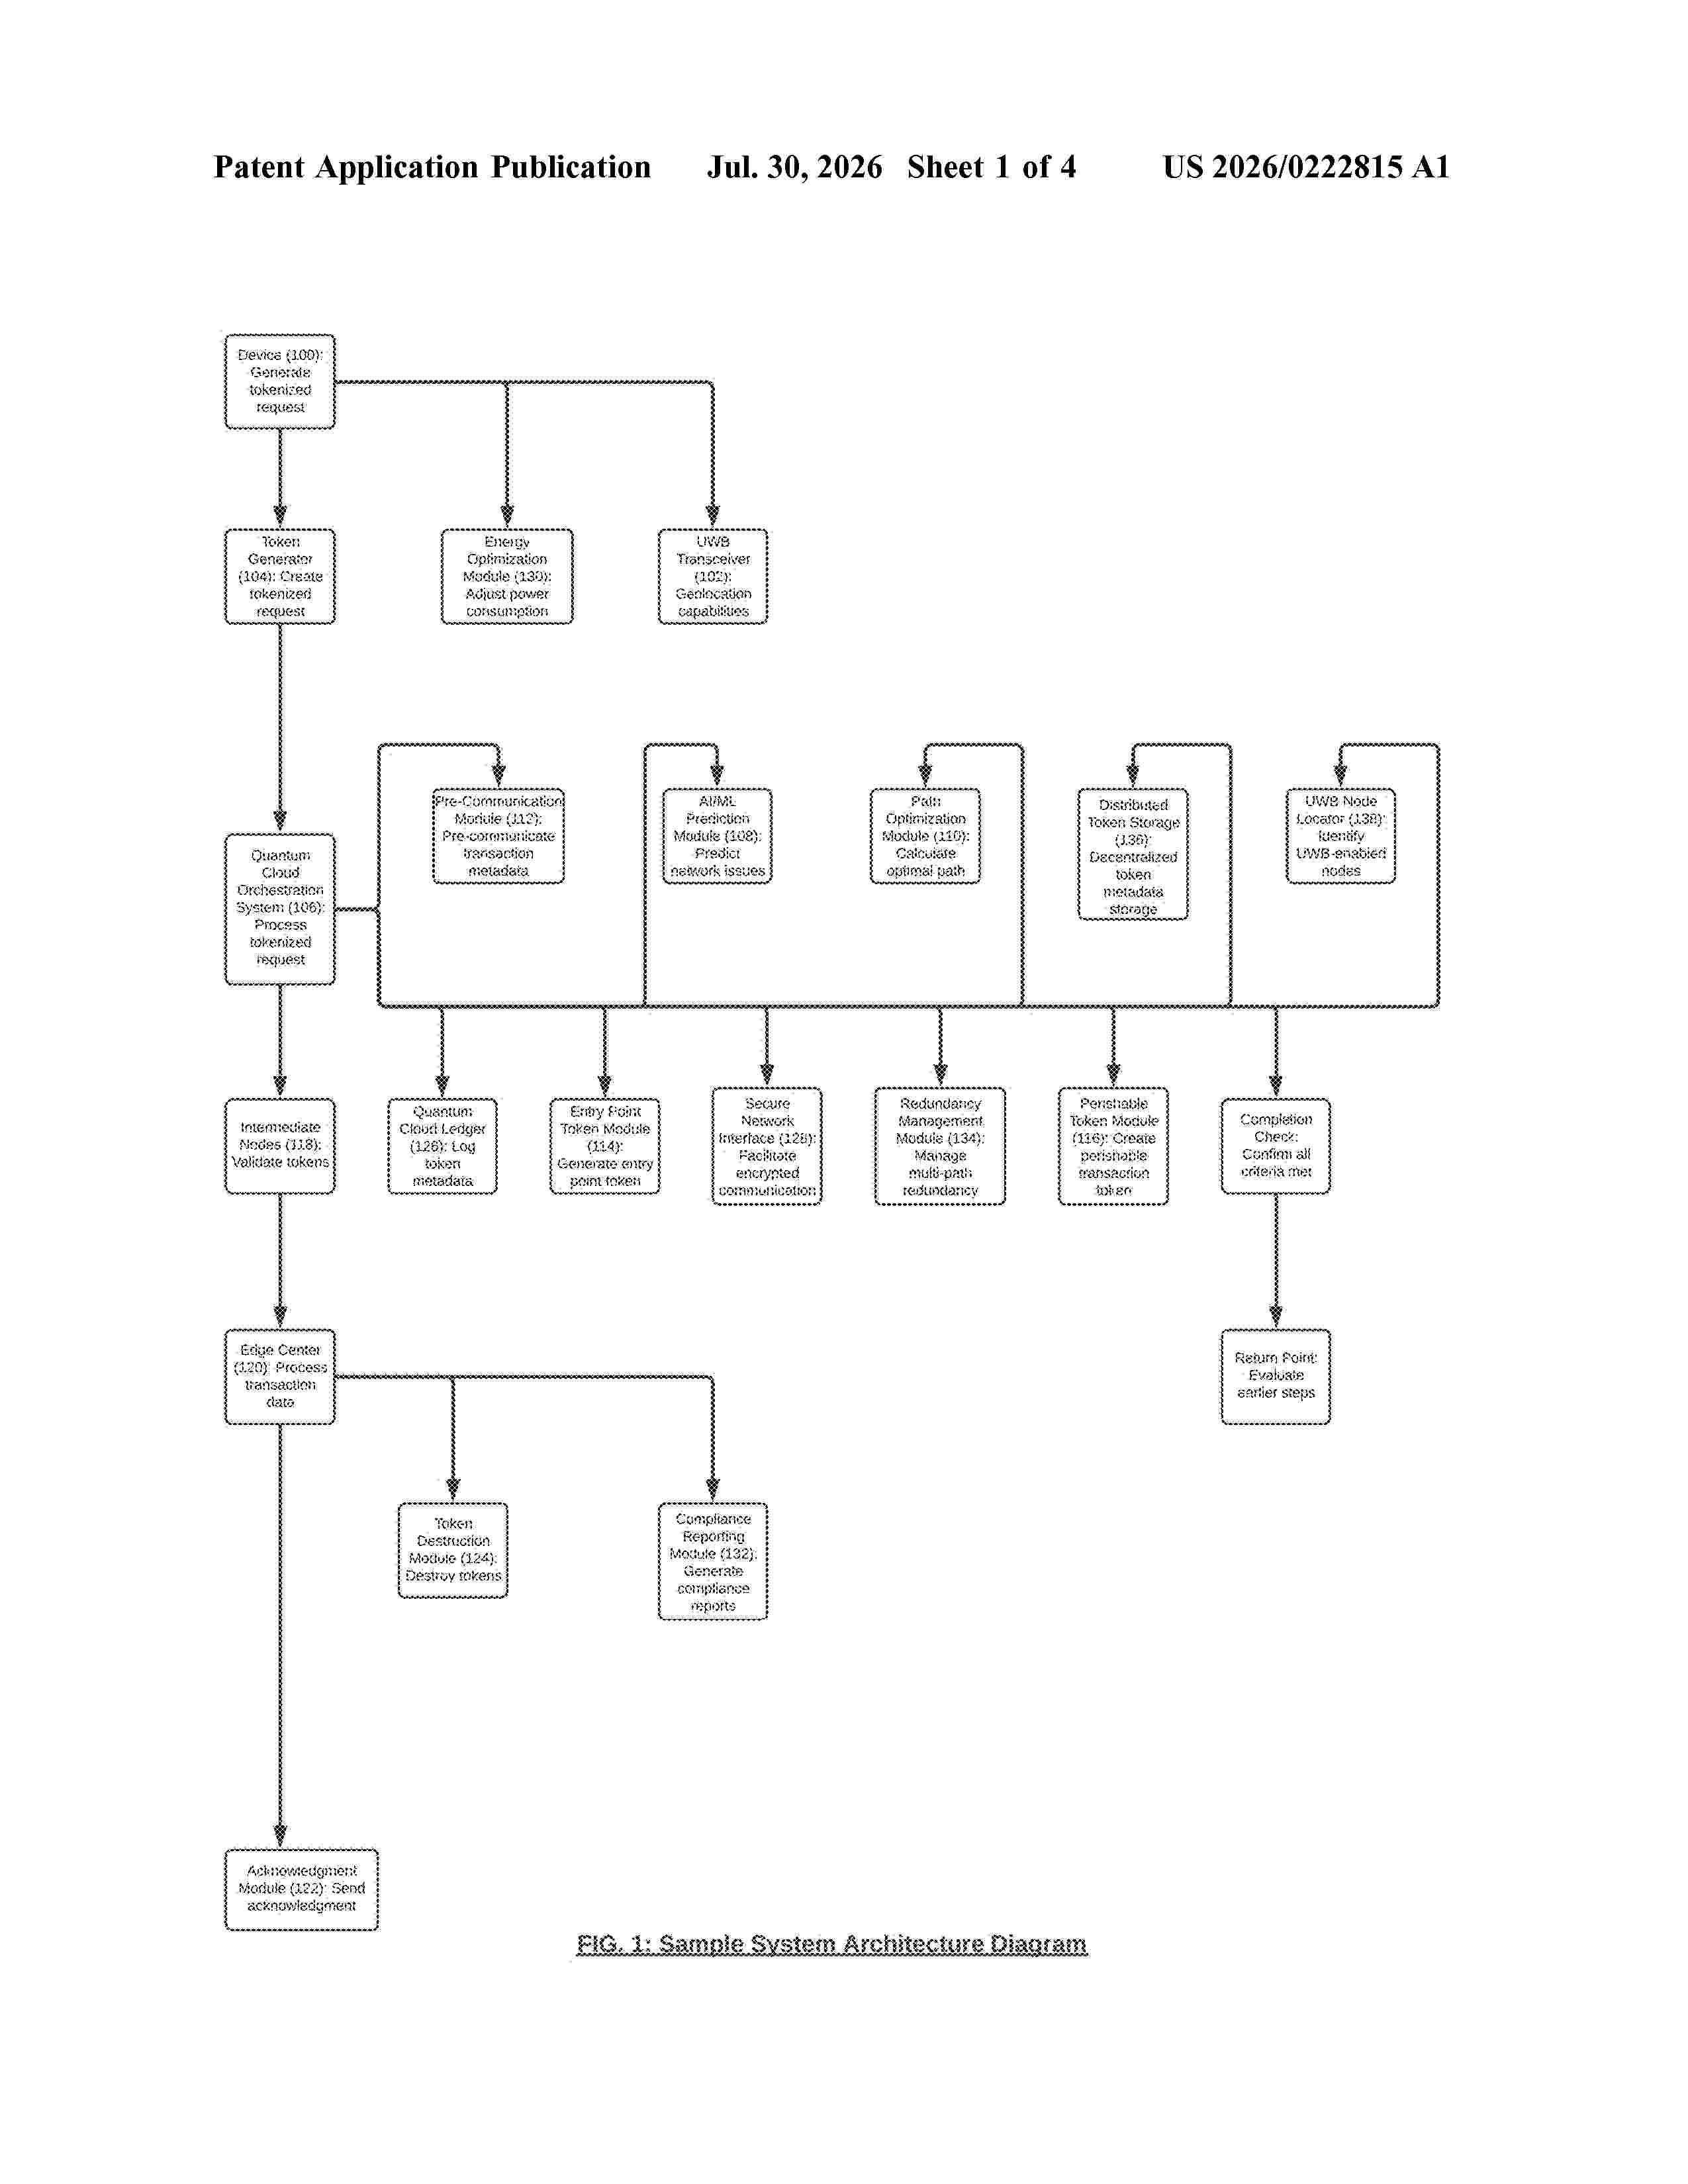
Resumen de: US20260222815A1
0000 An Ultra-Wide Band (UWB)-based communication framework integrates quantum cloud orchestration and tokenized security to enable secure, efficient, and low-latency transactions between devices and edge centers. The system dynamically generates quantum-encrypted, perishable tokens containing transaction metadata, including geolocation, network type, and security requirements, to optimize data transfer. The framework employs UWB technology for precise location tracking and low-energy communication, enabling seamless hybrid network integration across UWB, 5G, and Wi-Fi. The quantum cloud orchestrator leverages AI and machine learning to predict network conditions, optimize transaction paths, and pre-communicate metadata for real-time processing. Using Software-Defined Networking (SDN), the system ensures secure and efficient routing while maintaining compliance with regulatory standards. Applications span diverse sectors, including smart workplaces, contactless retail, dynamic ticketing, personalized hospitality, and emergency response coordination. This invention addresses critical challenges in signal strength, energy consumption, and latency, offering a scalable, transformative solution for secure and efficient device-edge communication.
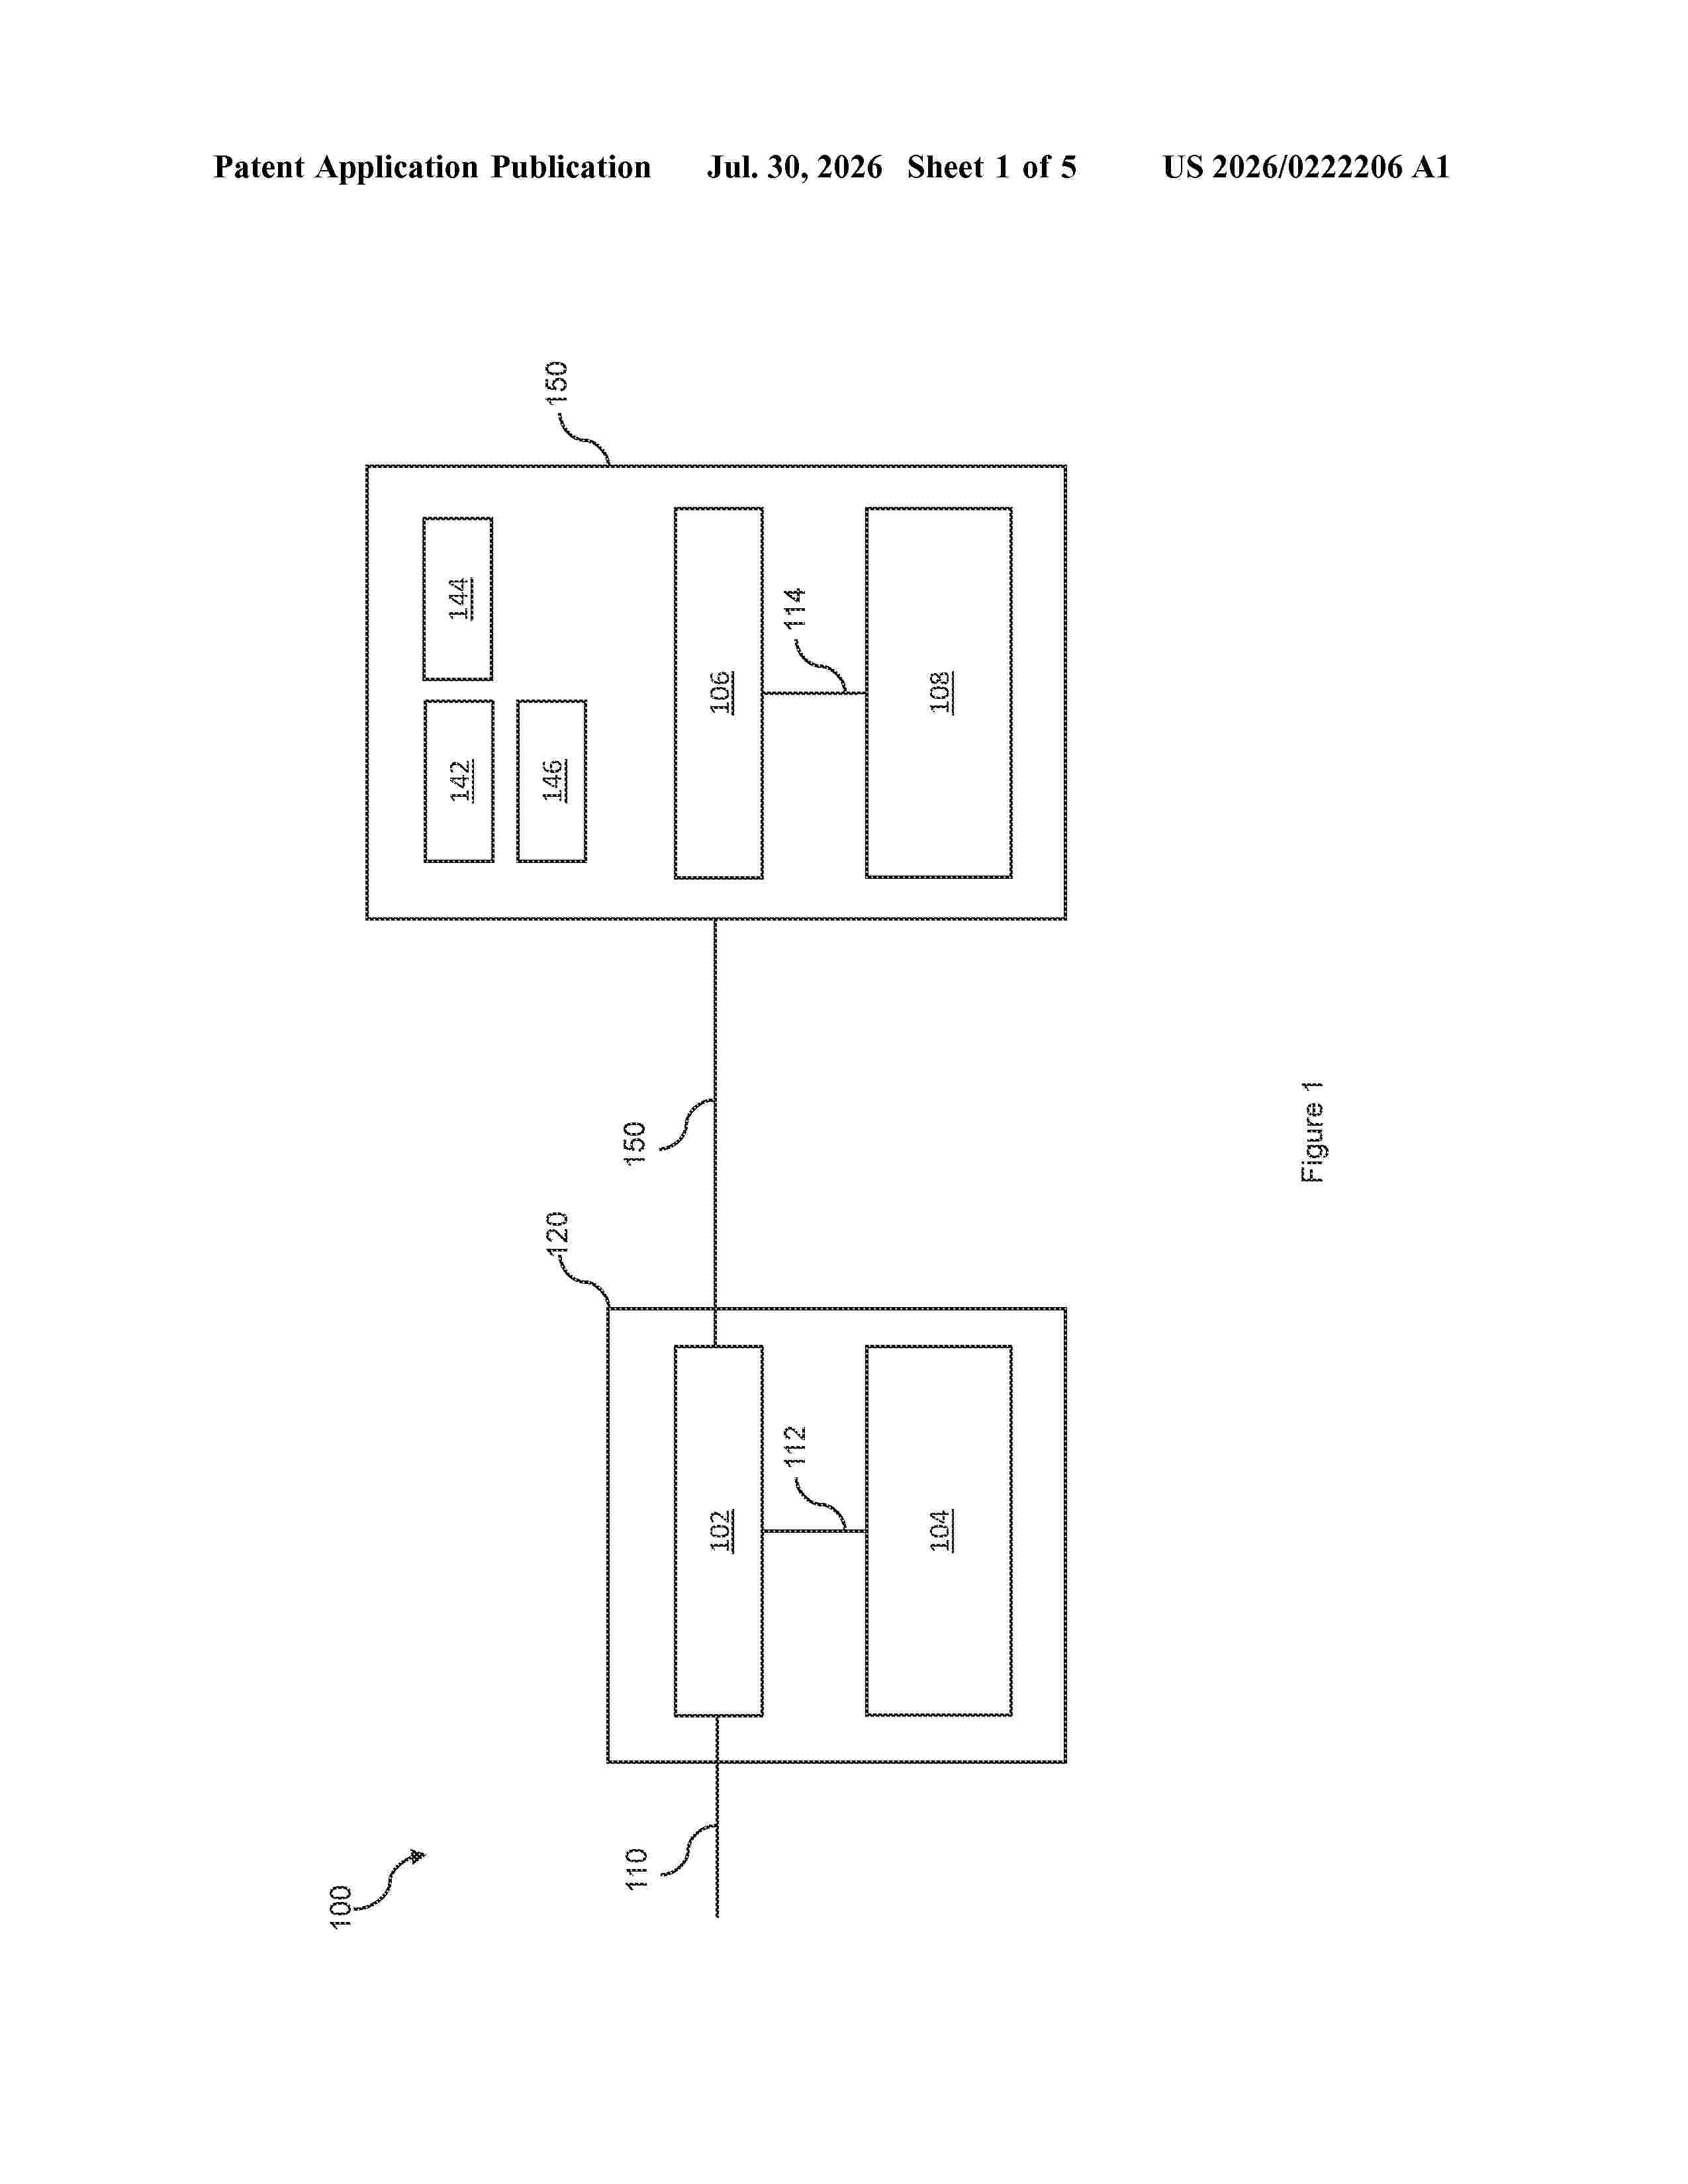
Resumen de: US20260222206A1
A quantum token generation method using computing system comprising a quantum computer in communication with a classical computer is provided. The method comprising the steps of: generating, using the classical computer, a unique identifier comprising f portions; determining, using the classical computer, a secret-key quantum circuit comprising n qubits; generating, using the classical computer and the quantum computer, a classical description of the unique identifier using the secret-key quantum circuit; wherein the classical description comprises n portions; generating, using an n-qubit quantum circuit of the quantum computer, a quantum state based on the classical description of the unique identifier; and outputting, using the classical computer, a quantum token, the quantum token comprising: the unique identifier; and the quantum state.
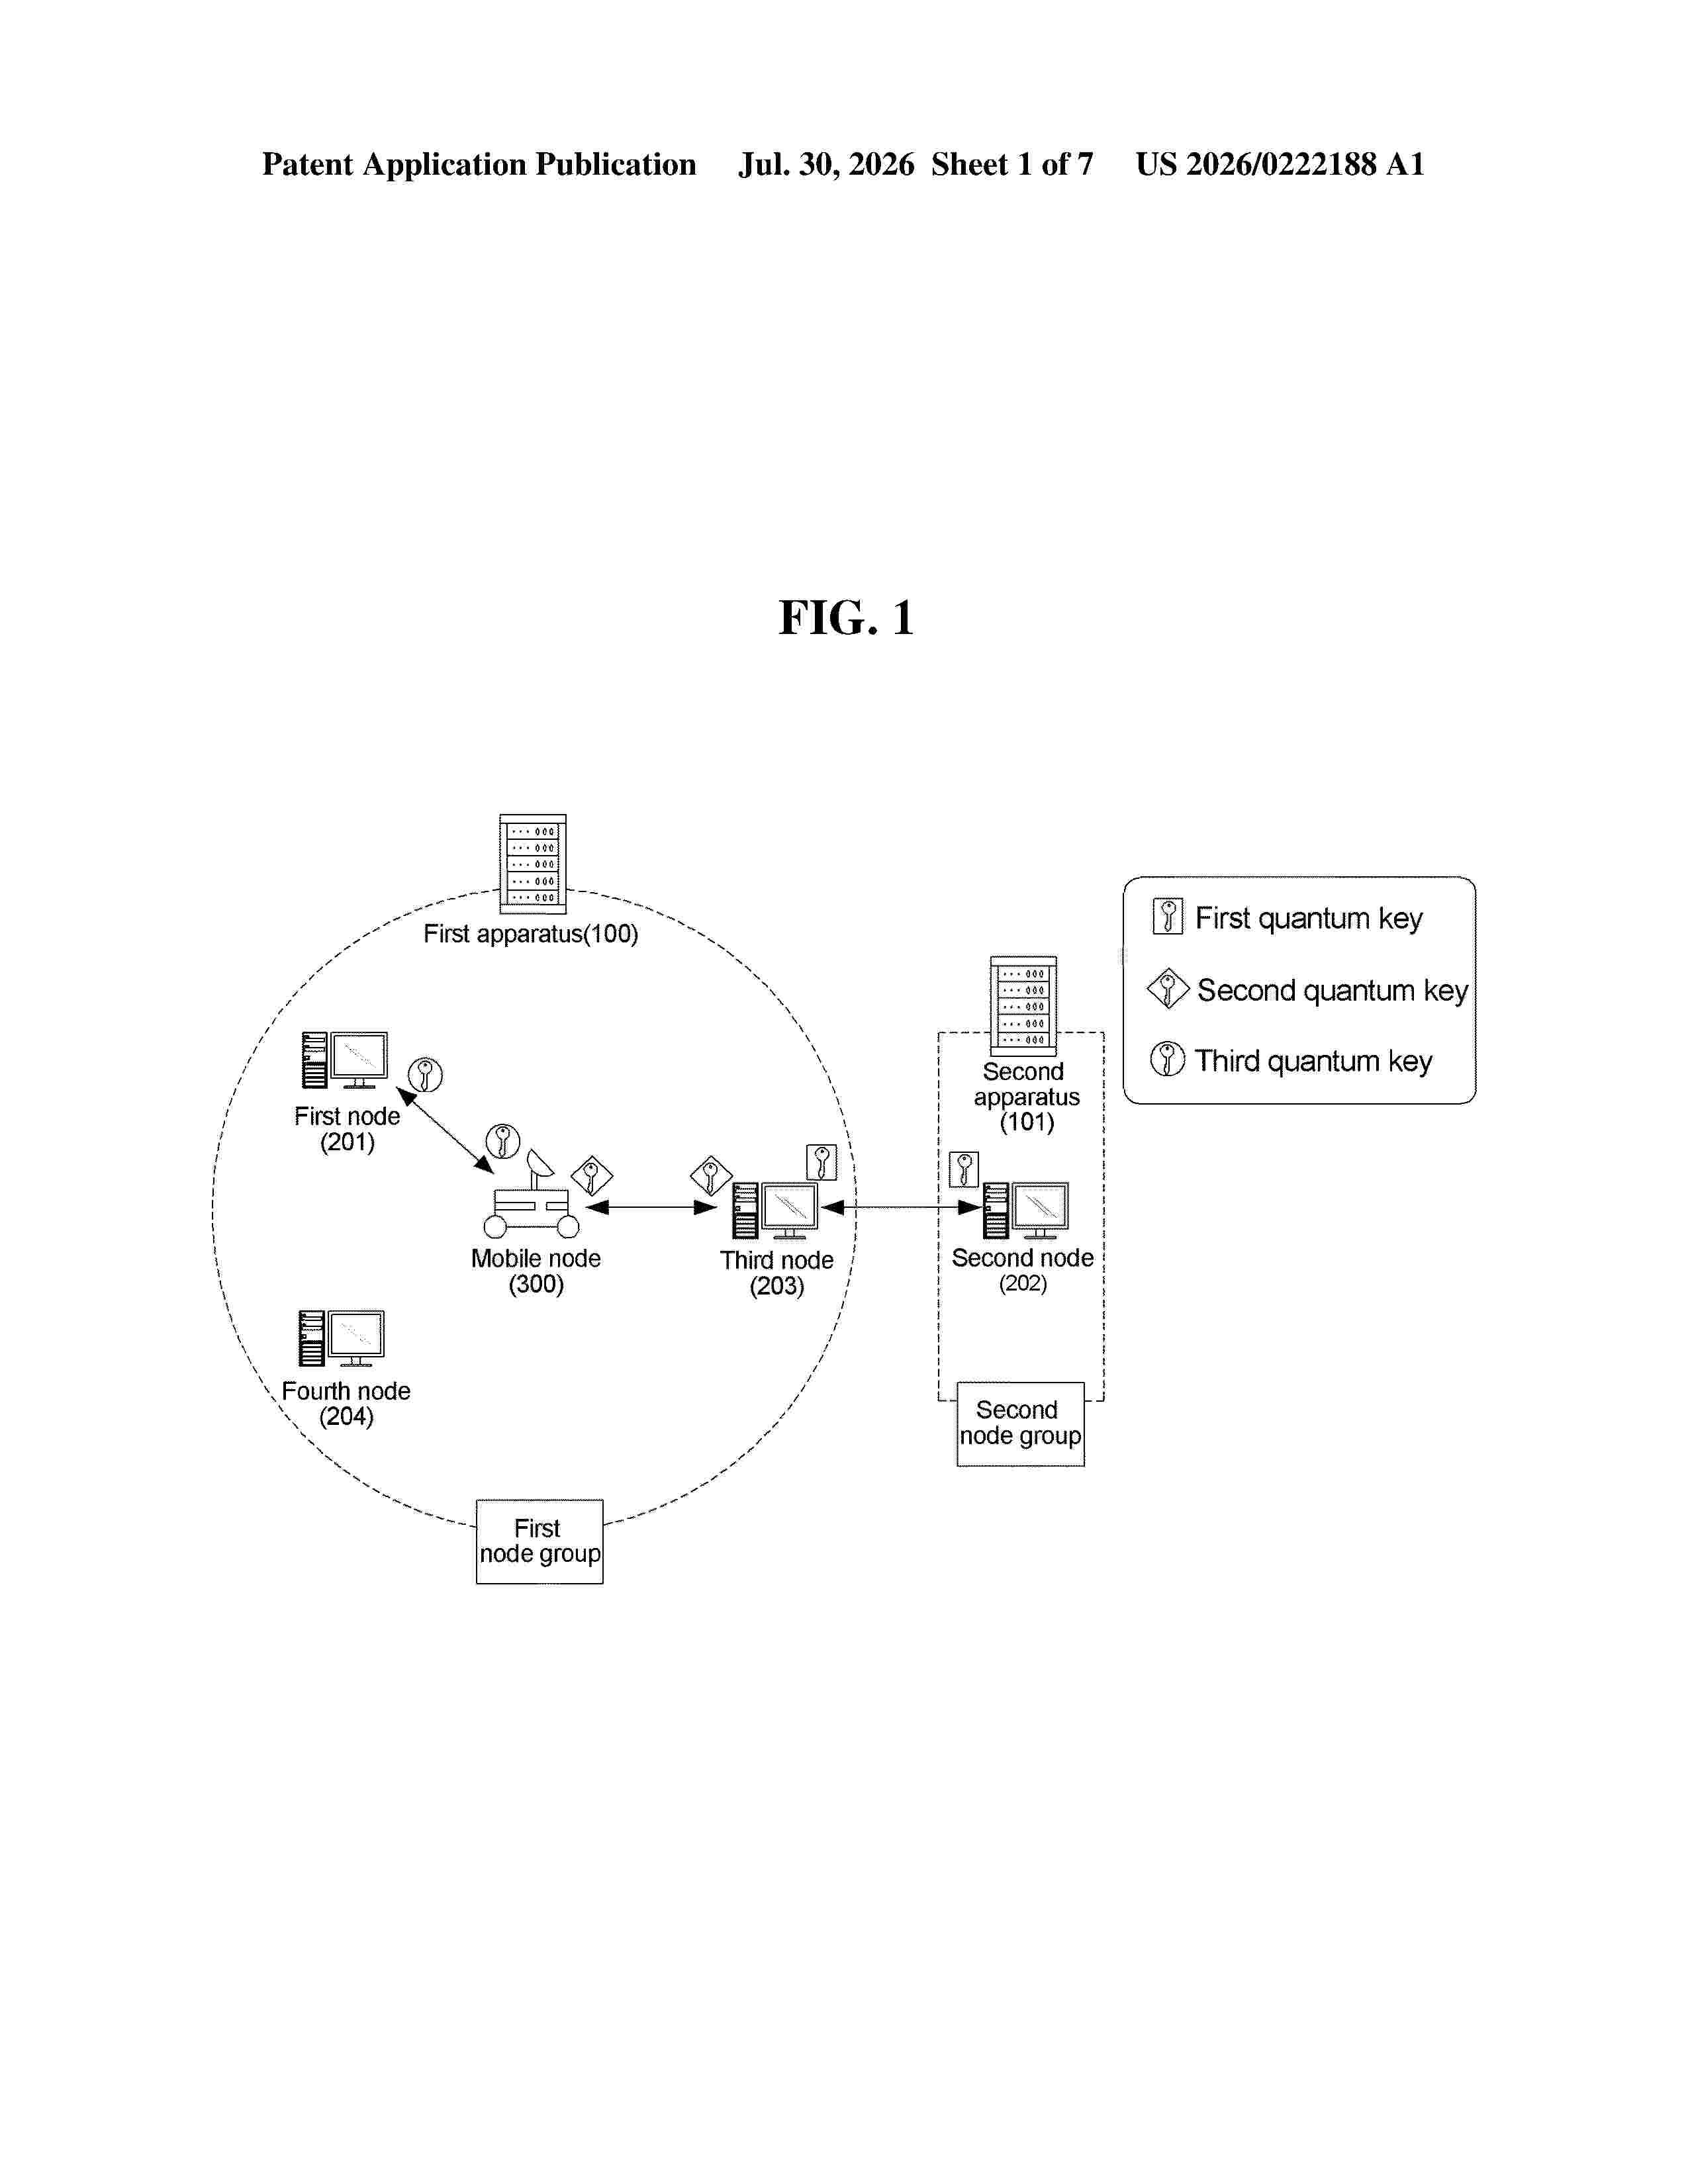
Resumen de: US20260222188A1
0000 A quantum key distribution (QKD) control apparatus may receive, from a first node in a first node group, a request for QKD with a second node in a second node group. The apparatus obtains information about an external QKD control apparatus managing the second node and determines a third node within the first node group that can connect to the second node. By requesting QKD between the second and third nodes through the external control apparatus, a first quantum key is generated. A mobile node is then moved to the third node to generate a first combined key and subsequently to the first node to generate a second combined key, enabling secure key sharing between the nodes.
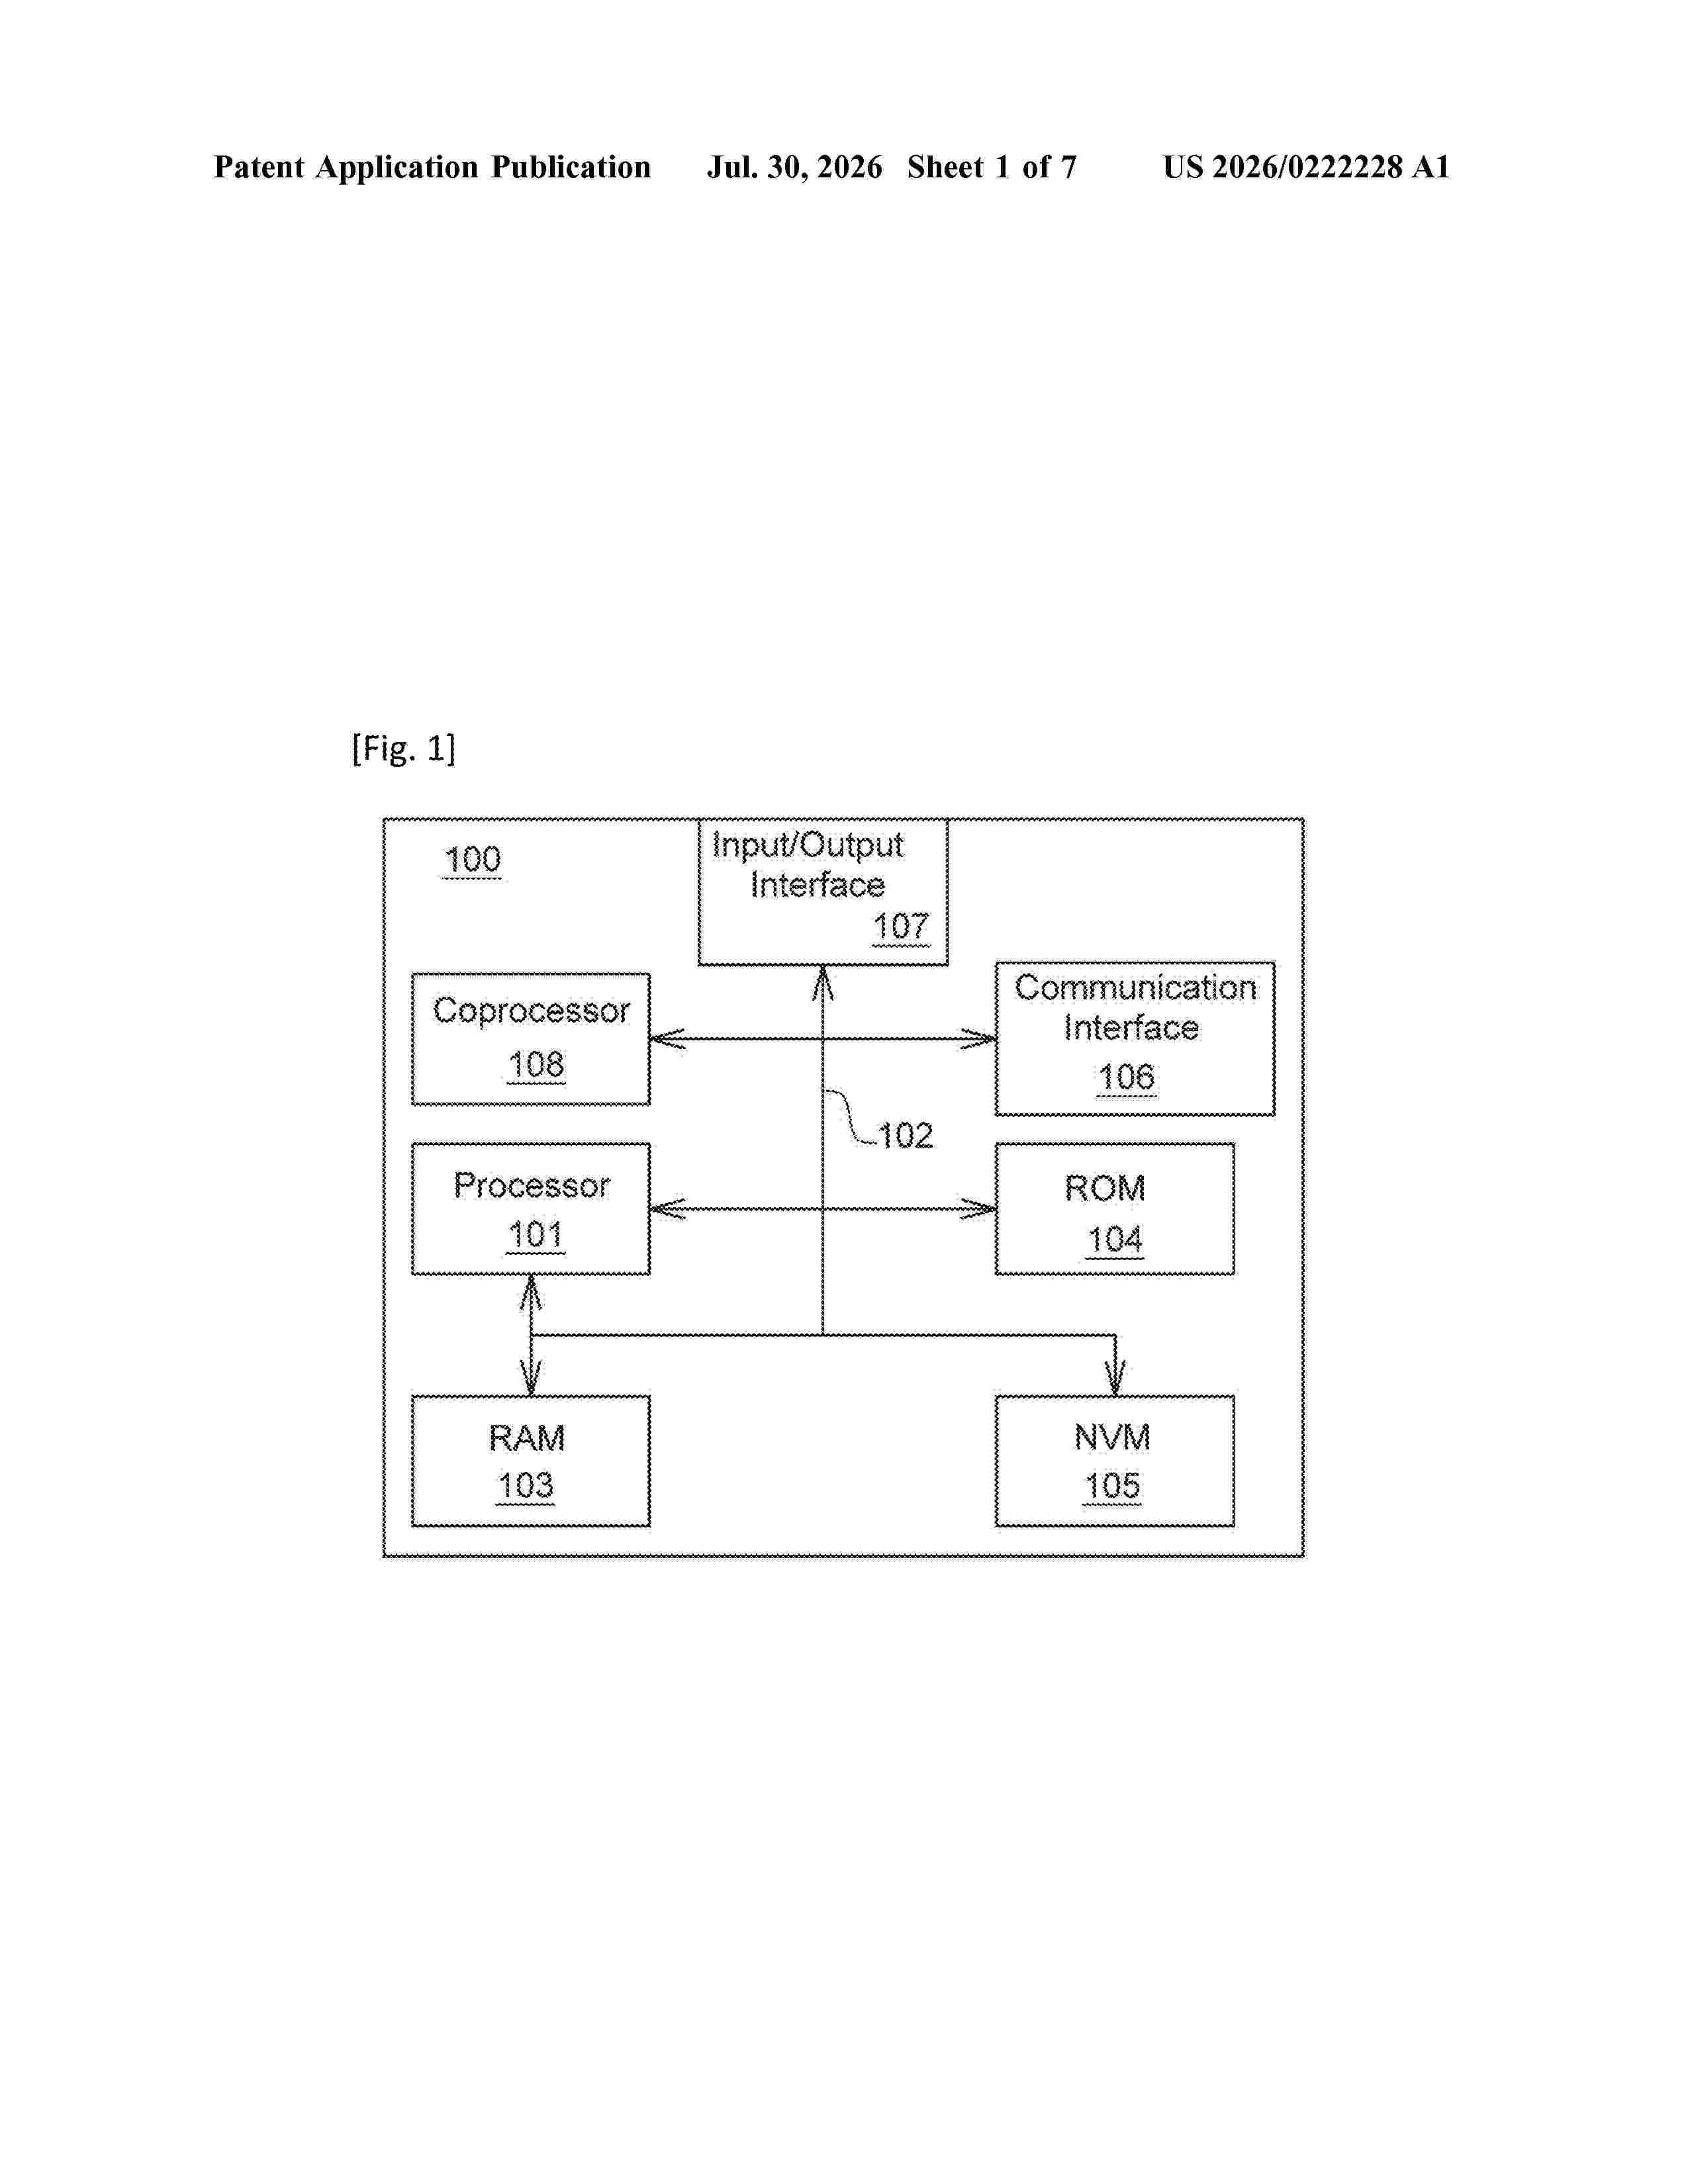
Resumen de: US20260222228A1
A method for optimizing the execution of the generation of a Crystals-Dilithium post-quantum digital signature σ=({tilde over (c)}, z, h) of a message M with a secret key sk=(ρ, K, tr, s1, s2, t0) where ρ, K, tr are 256 bits binary values, s1 and s2 are vectors of length l, respectively k, of elements of the ring Rq whose coefficients are lower than a first predetermined value η, and t0 is a polynomial vector of length k with k, l, n and q integers. Other aspects are described herein.
Resumen de: US20260222186A1
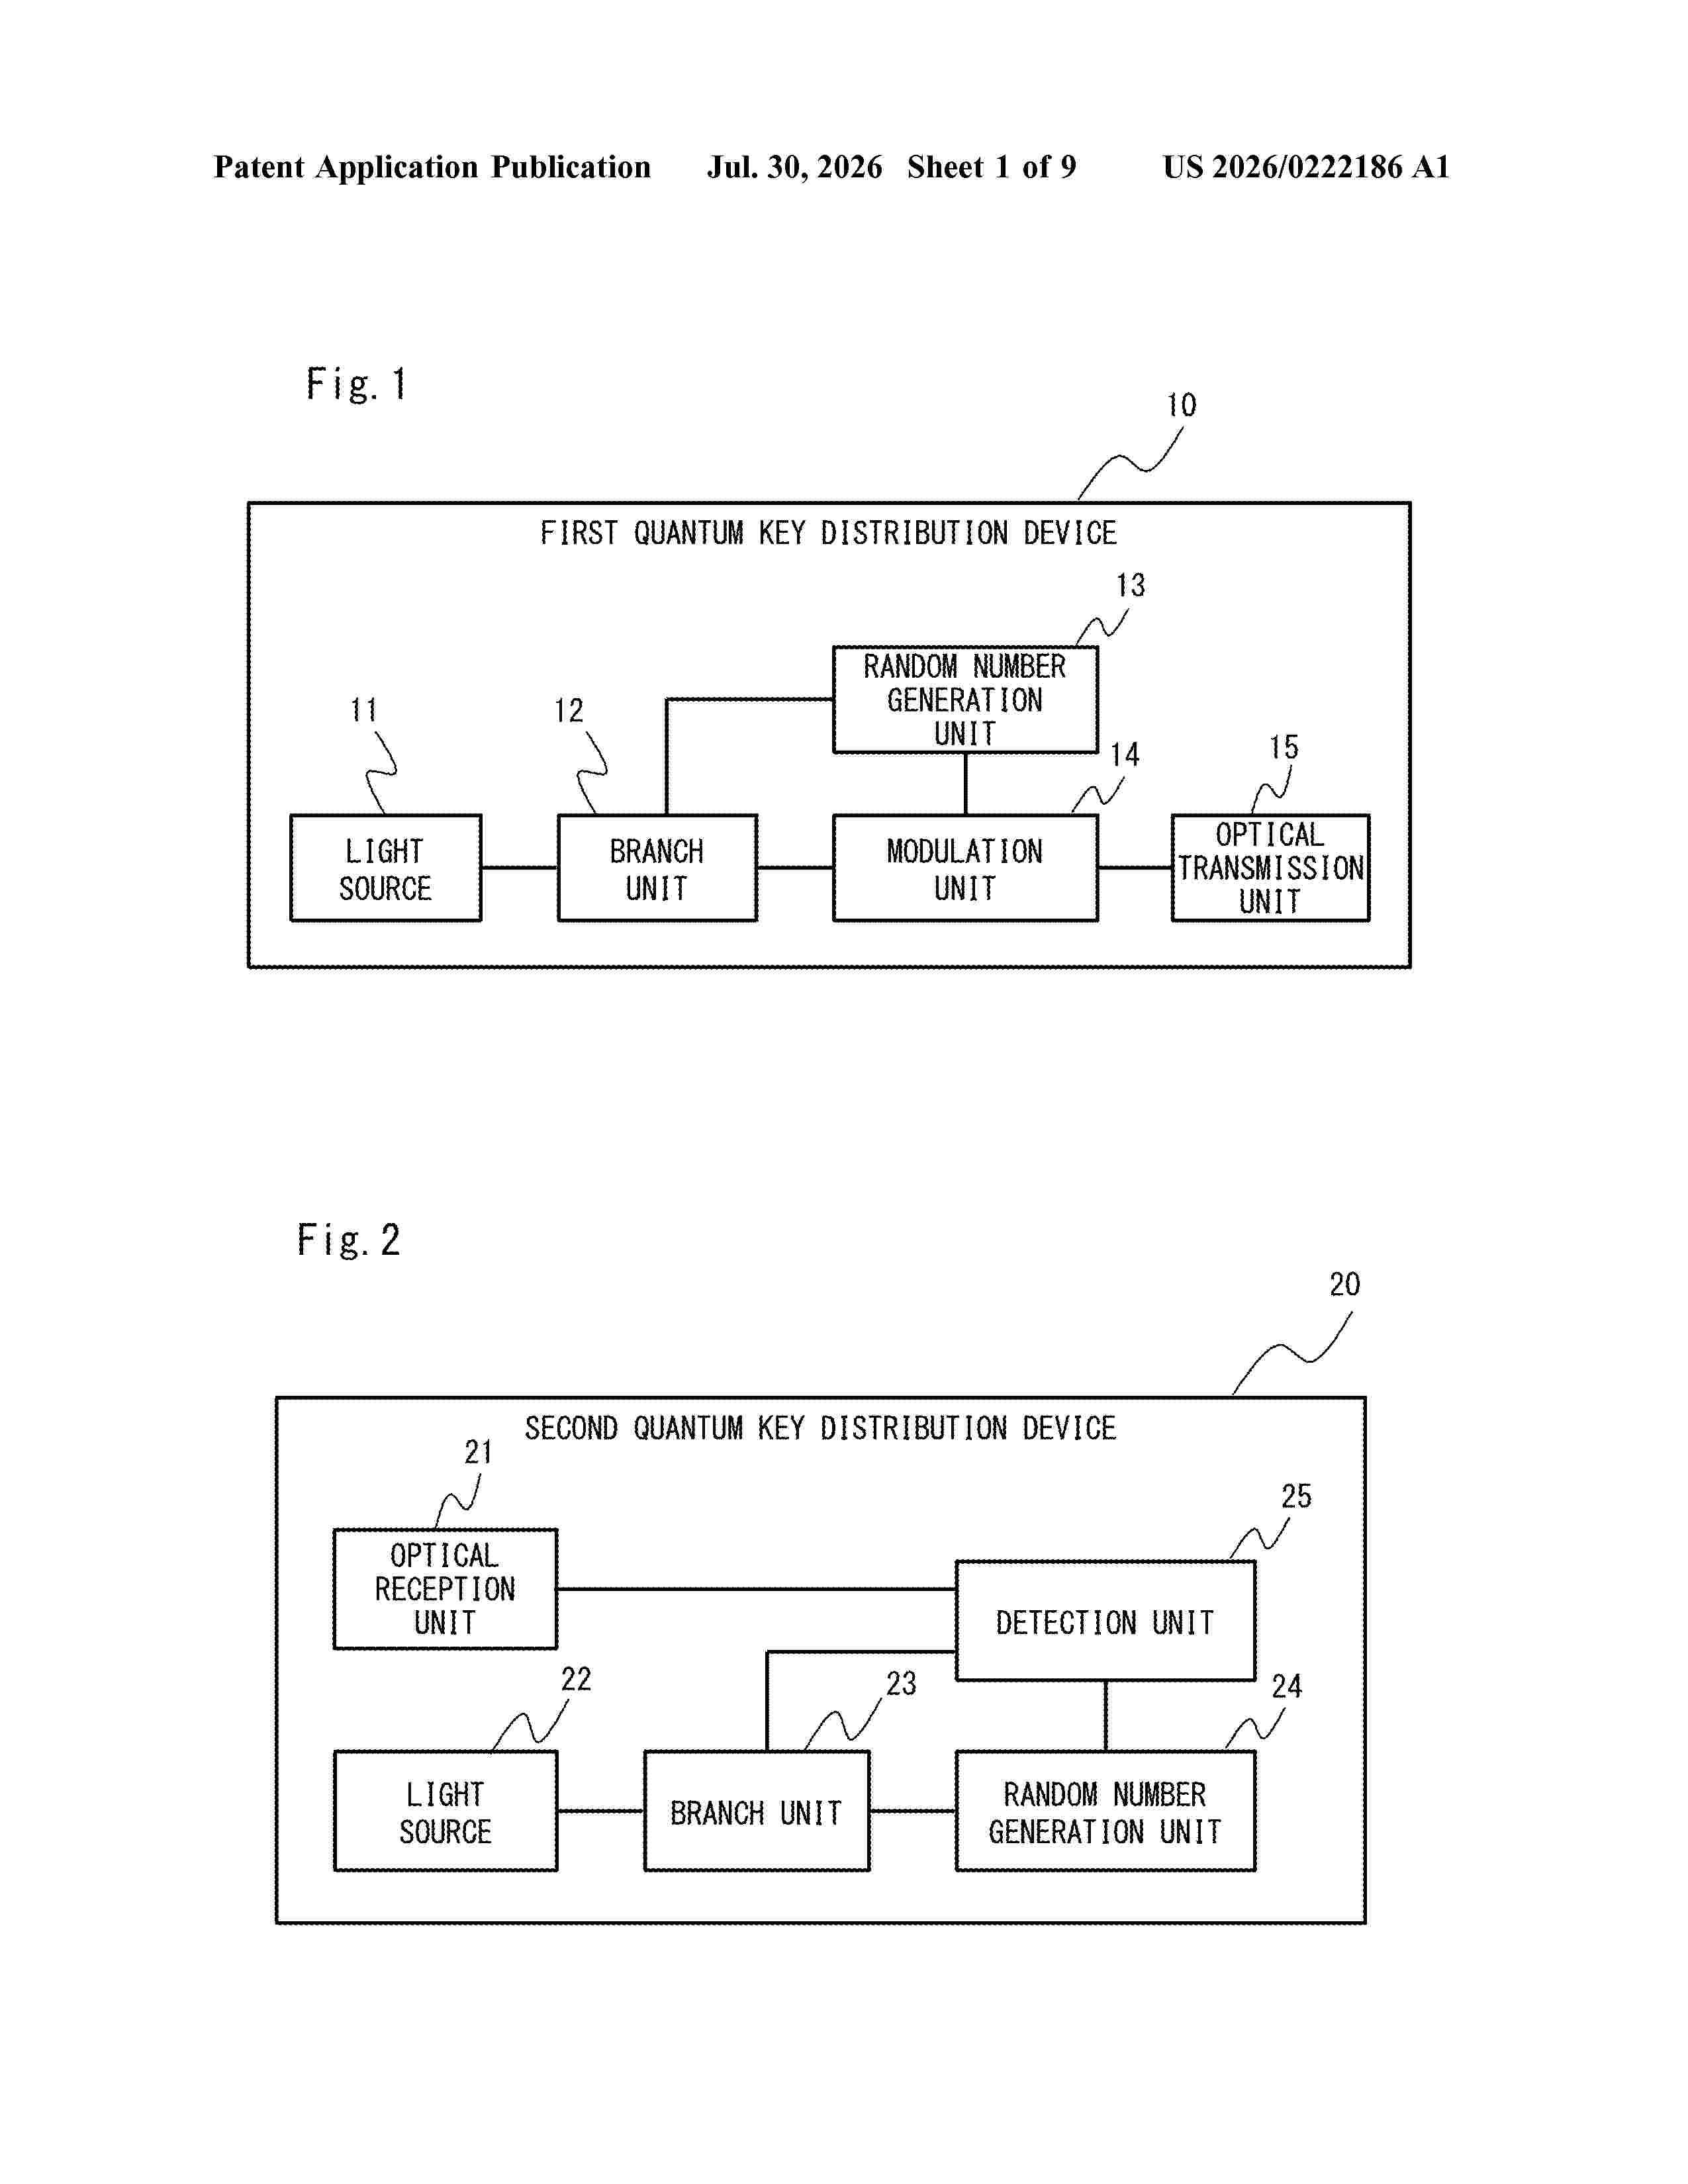
A first quantum key delivery device (10) comprises: a light source (11) that outputs light; a branch unit that causes light output from the light source (11) to branch to first light and second light; a random number generation unit (13) that generates a random number on the basis of the first light caused to branch by the branch unit (12); a modulation unit (14) that modulates the second light caused to branch by the branch unit (12) on the basis of the random number generated by the random number generation unit (13); and an optical transmission unit (15) that transmits the second light modulated by the modulation unit (14) as a quantum optical signal to another quantum key delivery device.
Resumen de: WO2025061836A1
The present invention relates to an integrated quantum random number generator, iQRNG, in particular a photonic QRNG which is monolithically scalable in a common semiconductor substrate in the same material system and constructed in a completely integrated manner, consisting of a photon source and a detector, coupled directly to the source, for individual photons in a particularly compact and attack-resistant design on a technology platform, open for diverse applications, for semiconductor structuring. The subject matter of the present invention is an integrated quantum random number generator, iQRNG, (200), comprising a photon source (120) and an individual photon detector (130), wherein the photon source (120) and the individual photon detector (130) are arranged in the vertical direction one above the other in a common substrate (110) made of a semiconductor material. The present invention also relates to an integrated electronic circuit (500) which comprises at least one iQRNG (200) according to the invention.
Resumen de: WO2025062472A1
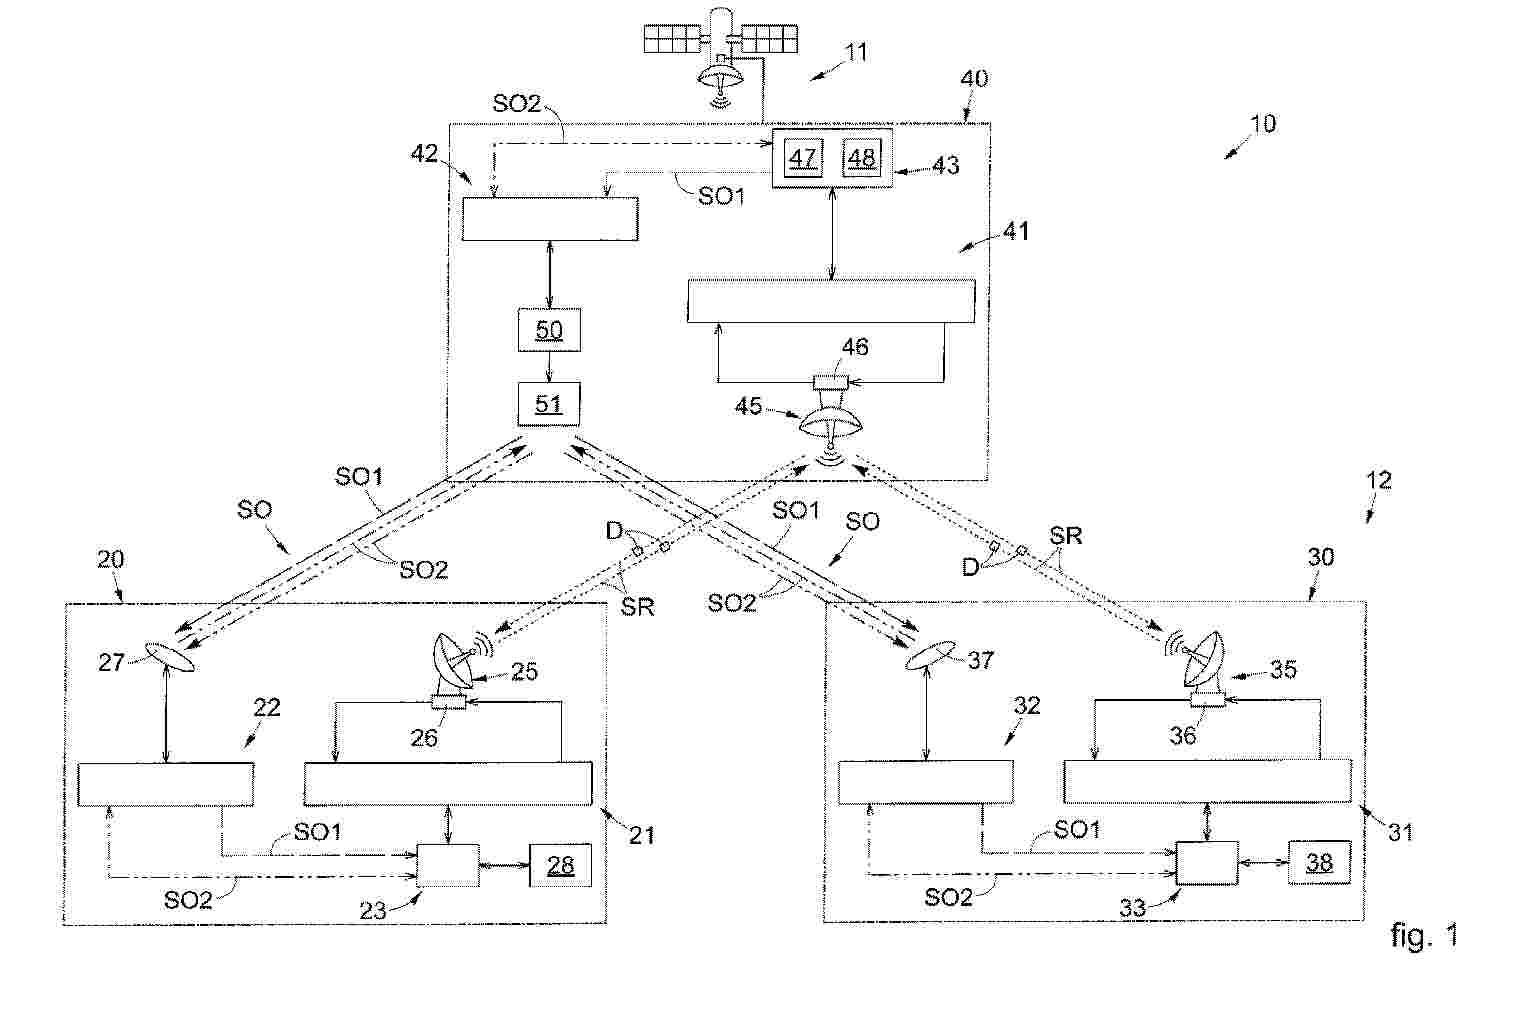
Data (D) transmission system (10) via satellite (11), comprising at least one satellite station (40) disposed on a respective satellite (11) with which a first transmission station (20) and a second transmission station (30) are operatively connected, during use, wherein at least one of either the first (20) or the second station (30) is disposed, during use, on a mobile means of transport (12), the other being disposed on a respective mobile means of transport (12) or on a fixed point on land. The stations (20, 30, 40) comprise, respectively, at least an optical assembly (22, 32, 42) configured to transmit and/or receive one or more optical signals (SO) comprising at least a first type of optical signal (SOI) to allow the quantum distribution of encryption keys, and a transmission assembly (21, 31, 41) configured to transmit and receive one or more radio frequency signals (SR) containing data (D), wherein said optical assemblies (22, 32, 42) and said radio frequency transmission assemblies (21, 31, 41) are configured to transmit and/or receive respective pointing signals to achieve an alignment between the stations (20, 30, 40).
Resumen de: EP4783514A1
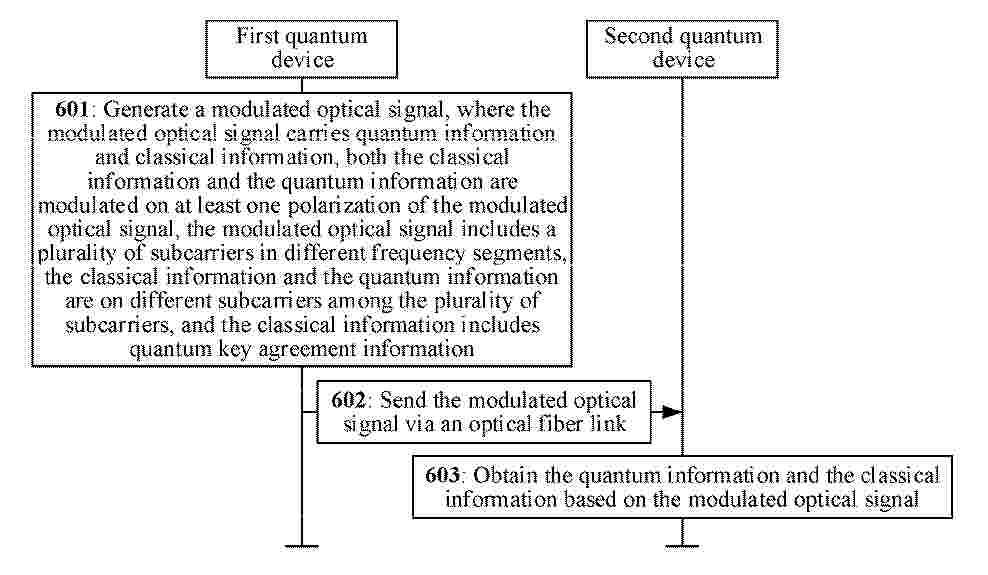
This application discloses a quantum key distribution method, apparatus, and system, relating to the field of network technologies. A first quantum device generates a modulated optical signal that carries quantum information and classical information. Both the classical information and the quantum information are modulated on at least one polarization of the modulated optical signal, the modulated optical signal includes a plurality of subcarriers in different frequency segments, the classical information and the quantum information are on different subcarriers among the plurality of subcarriers, and the classical information includes quantum key agreement information. The first quantum device sends the modulated optical signal to a second quantum device via an optical fiber link. By modulating the quantum information and the classical information on the same polarization of the optical signal, a system achieves a high capacity. The quantum information and the classical information are modulated on subcarriers in different frequency segments within the optical signal, so that respective modulation accuracy requirements of a classical signal and a quantum signal can be satisfied. Reusing a set of devices to transmit both the quantum information and the classical information reduces hardware costs.
Resumen de: KR20260117471A
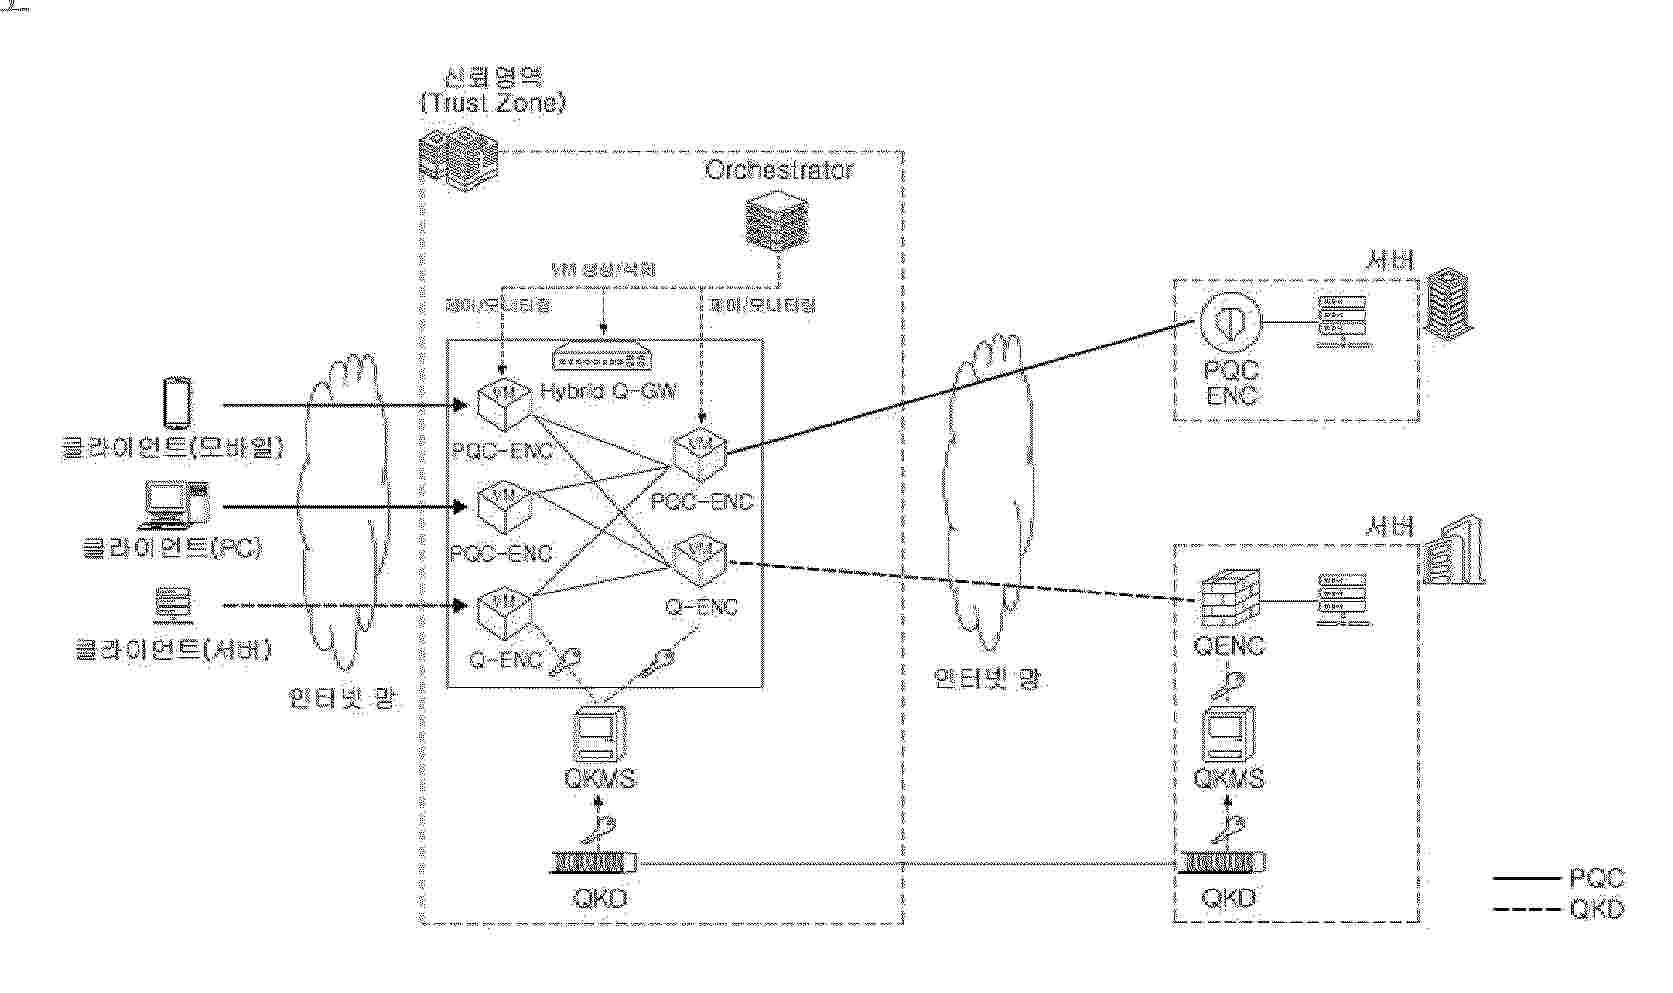
0001a 본 발명은 PQC 및 QKD 하이브리드 네트워크에서의 암호화 데이터 전송 방법, 장치 및 컴퓨터 프로그램에 관한 것으로, 본 발명의 PQC 및 QKD 하이브리드 네트워크에서의 암호화 데이터 전송 방법은, 제1 암호화기에서 제1 암호화 처리된 제1 암호화 데이터를 수신하는 단계; 제1 암호화 데이터를 제1 암호화 메모리에 전달하는 단계; 제1 암호화 메모리에서 제1 암호화 데이터를 제1 복호화 처리하는 단계; 제1 암호화 메모리에서 제1 복호화 처리된 제1 복호화 데이터를 제2 암호화 처리하는 단계; 및 제2 암호화 처리된 제2 암호화 데이터를 제2 암호화기에 전송하는 단계;를 포함하는, 방법을 제시한다.
Resumen de: EP4783040A1
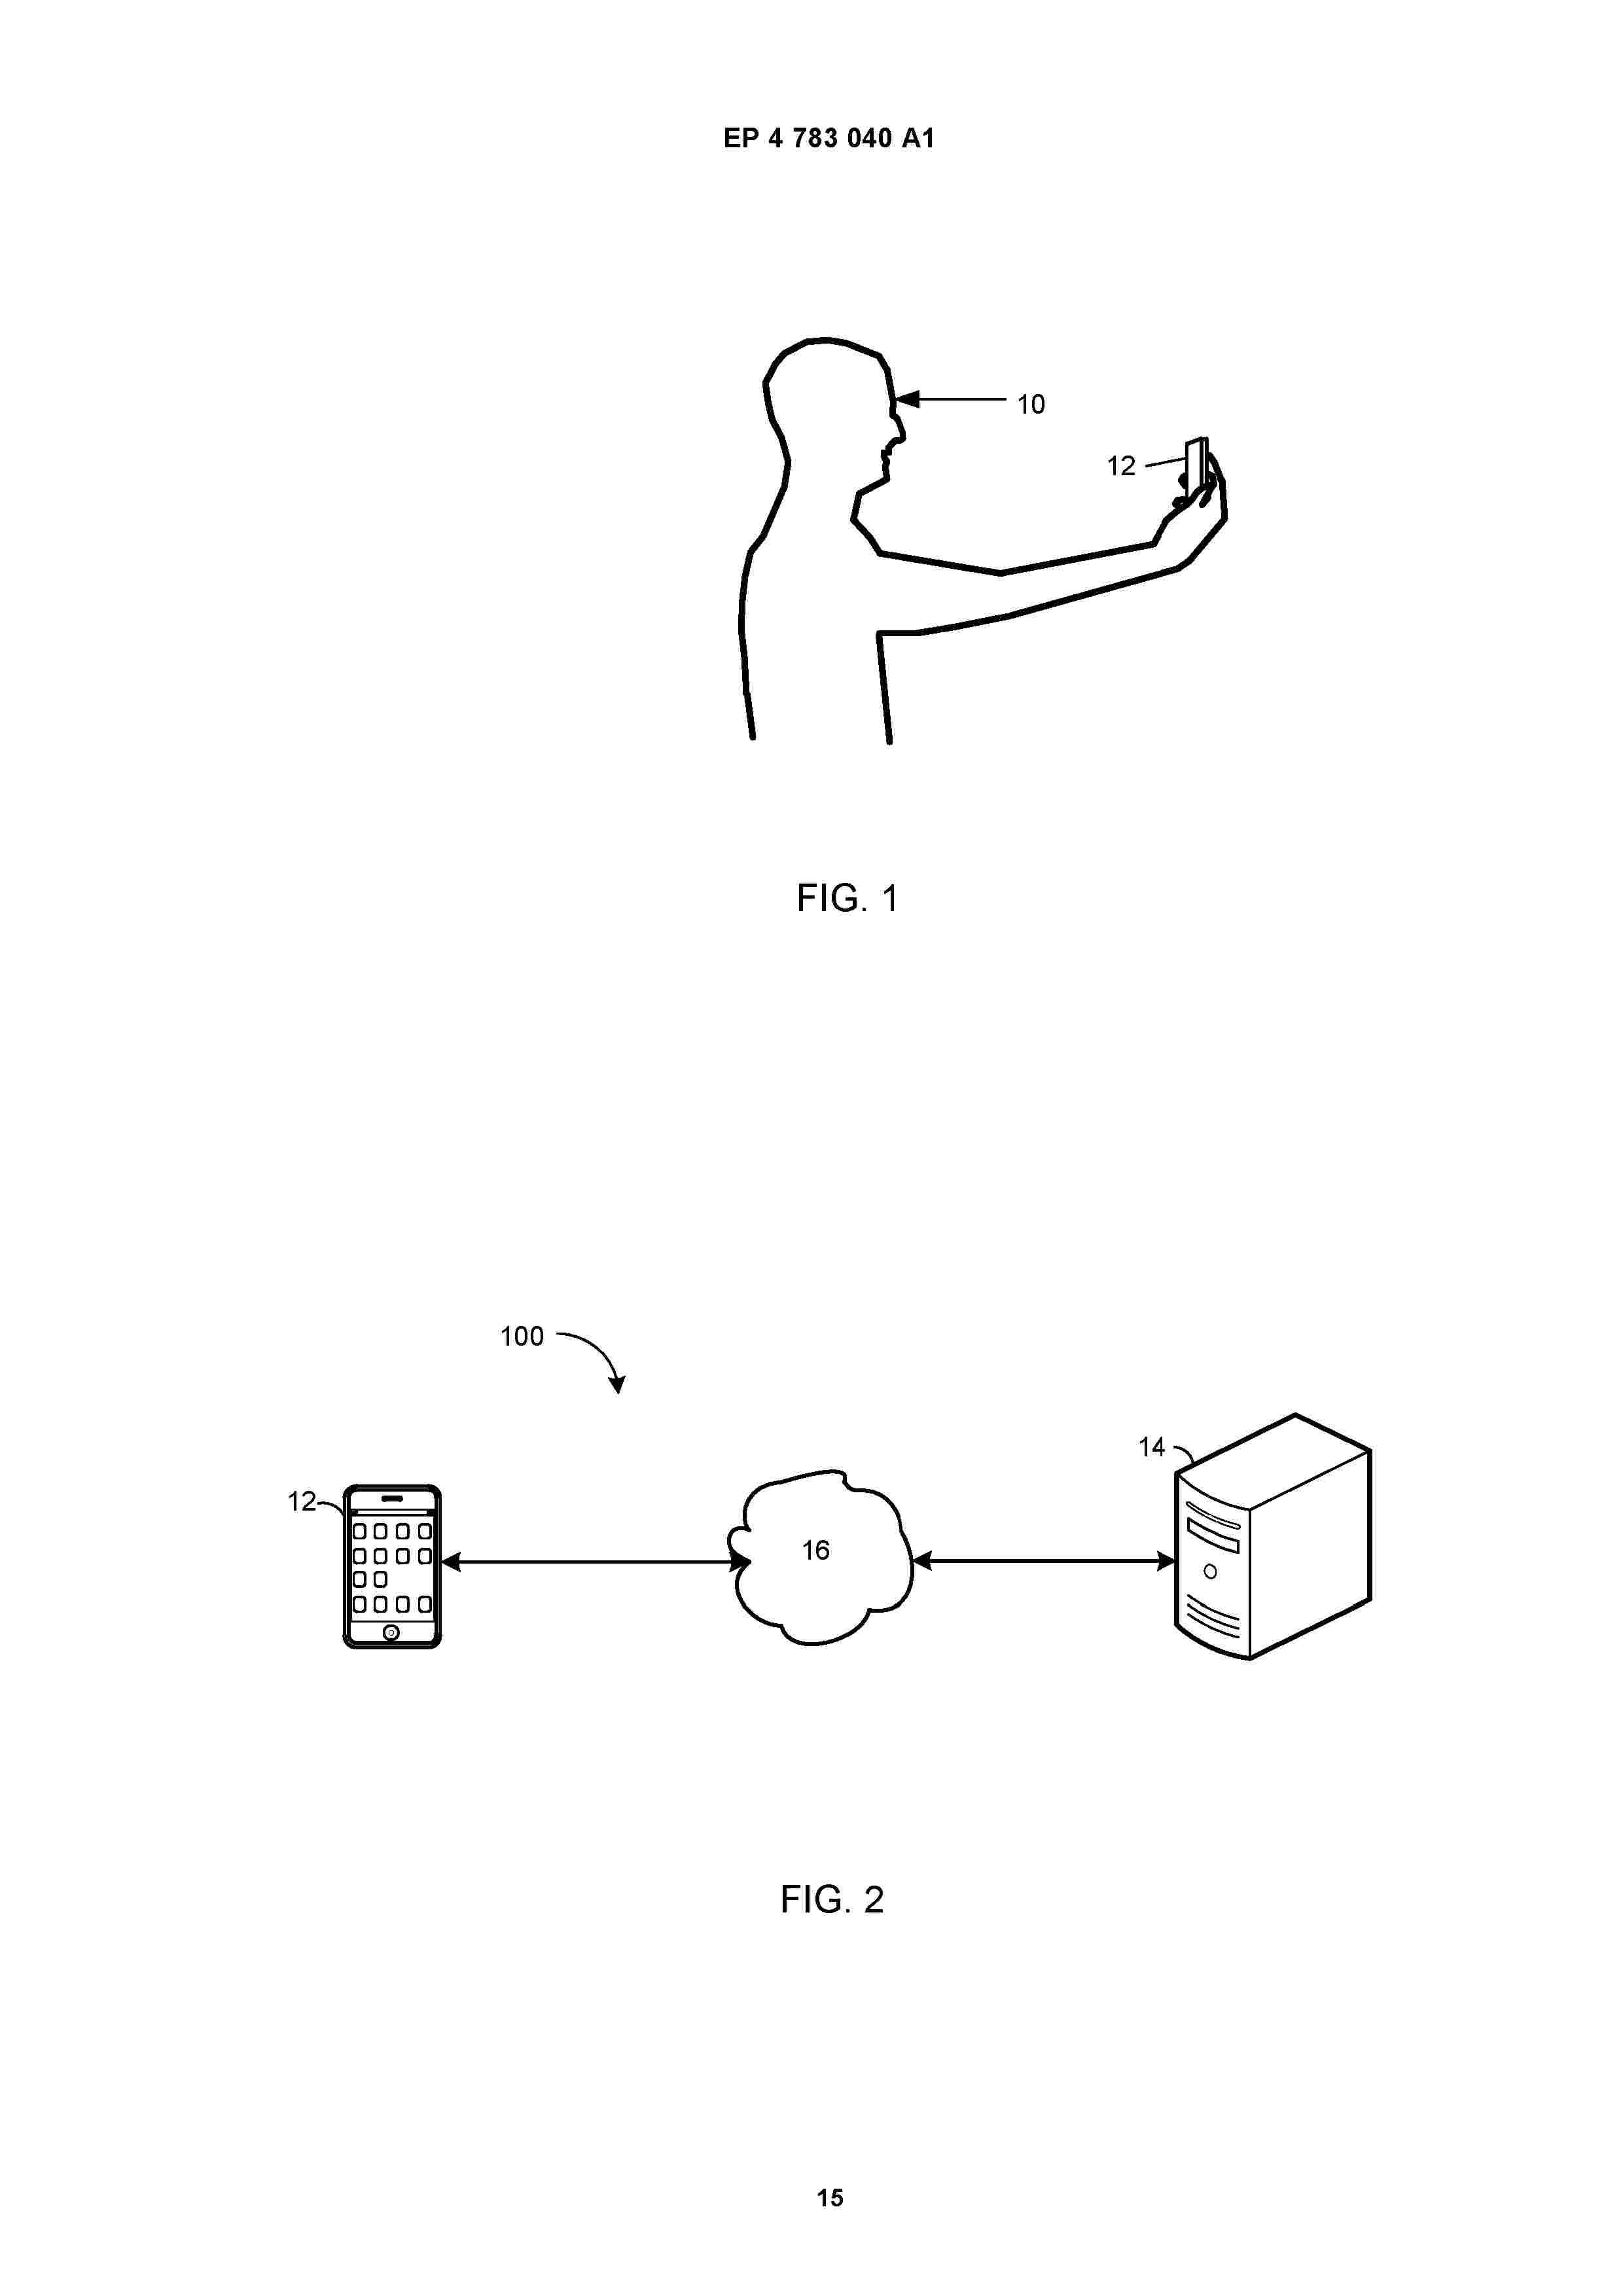
0001 A method for enhancing detection of fraudulent authentication data includes receiving, by an electronic device, data during an authentication transaction, computing a feature vector from the received data, and normalizing the feature vector. The method also includes encoding the normalized feature vector into qubits, expanding, using at least one quantum algorithm, the normalized feature vector into a high-dimensional space, and detecting in the high-dimensional space anomalies indicative of fraud based on the qubits. Furthermore, the method includes calculating, based on the detected anomalies, a confidence score reflecting a likelihood that the received data is genuine and comparing the confidence score against a threshold value. In response to determining the confidence score fails to satisfy the threshold value, the method determines that the received data requires secondary authentication.
Resumen de: CN122475859A
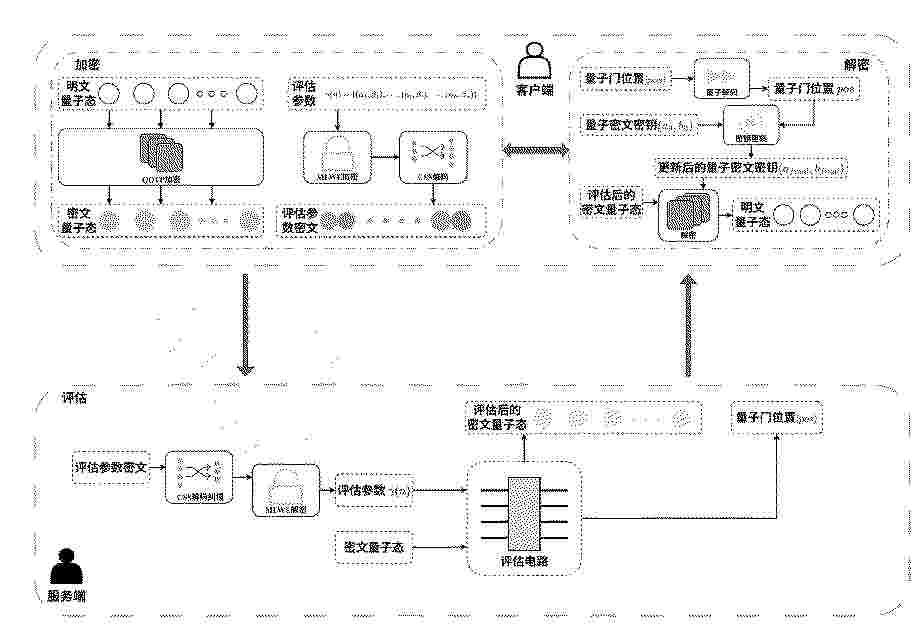
The invention relates to a quantum homomorphic encryption method based on MLWE encryption and CSS coding, and the method comprises the steps: carrying out the plaintext quantum encryption operation at a client, and obtaining a ciphertext quantum state; an evaluation parameter is generated at the client, MLWE encryption and CSS coding operation are carried out, and an evaluation parameter ciphertext quantum state is obtained; the server receives the evaluation parameter ciphertext quantum state, and performs CSS decoding and MLWE decryption operation to obtain an evaluation parameter; the server performs quantum circuit operation on the ciphertext quantum state according to the evaluation parameter, obtains the evaluated ciphertext quantum state, and records a quantum gate and an operation position thereof; and the client updates the key according to the quantum gate recorded by the server and the operation position of the quantum gate, and decrypts the evaluated ciphertext quantum state to obtain a plaintext. According to the method, the security and fault-tolerant capability of quantum homomorphic encryption can be improved, the data privacy is ensured, and meanwhile, the direct quantum calculation on the ciphertext is supported, so that the method is a beneficial supplement in the field of quantum security calculation.
Resumen de: CN122475862A
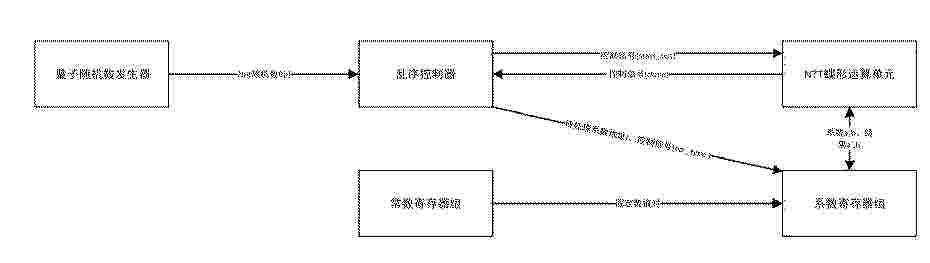
The invention discloses a quantum random number-based NTT module side channel defense method and an implementation circuit, and the method comprises the steps: dividing a plurality of butterfly operations of each level in NTT operation into a plurality of groups for scheduling execution, and distributing a two-bit random number for each group; and according to the value of the two-bit random number, respectively determining the execution opportunity of each group of butterfly operations or whether pseudo operations are inserted according to a preset scheduling rule. The implementation circuit comprises a quantum random number generator, an out-of-order controller, a constant register set, a coefficient register set and an NTT butterfly operation unit. According to the method, by randomizing the operation time sequence and inserting the pseudo operation which is difficult to distinguish in statistics, the side channel attack based on power consumption analysis is effectively resisted, the hardware overhead is small, the random number consumption is low, and the method is particularly suitable for embedded password equipment with limited resources.
Resumen de: CN122475863A
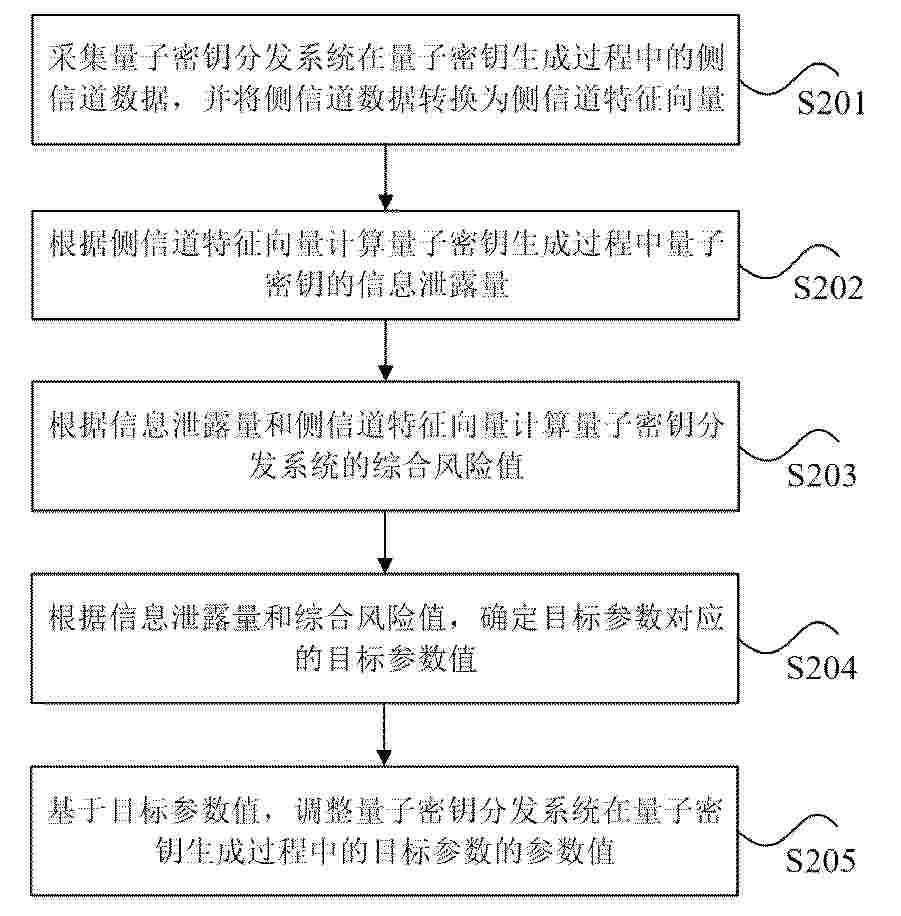
The invention discloses an adaptive security control method and device for a quantum key distribution system, and a storage medium. Relates to the technical field of quantum key distribution, and the method comprises the following steps: collecting side channel data of a quantum key distribution system in a quantum key generation process, and converting the side channel data into a side channel feature vector; calculating the information leakage amount of the quantum key in the quantum key generation process according to the side channel feature vector; calculating a comprehensive risk value of the quantum key distribution system according to the information leakage amount and the side channel feature vector; determining a target parameter value corresponding to the target parameter according to the information leakage amount and the comprehensive risk value; and adjusting a parameter value of a target parameter of the quantum key distribution system in the quantum key generation process based on the target parameter value. According to the method and the device, the problem of poor security of the quantum key distribution system in the key generation process due to the fact that the leakage amount cannot be accurately quantified in the related technology is solved.
Nº publicación: CN122475889A 28/07/2026
Solicitante:
ZHONGKE YUNCHAO BEIJING QUANTUM TECH CO LTD
INST INF ENG CAS
\u4E2D\u79D1\u4E91\u949E\uFF08\u5317\u4EAC\uFF09\u91CF\u5B50\u79D1\u6280\u6709\u9650\u516C\u53F8
\u4E2D\u56FD\u79D1\u5B66\u9662\u4FE1\u606F\u5DE5\u7A0B\u7814\u7A76\u6240
Resumen de: CN122475889A
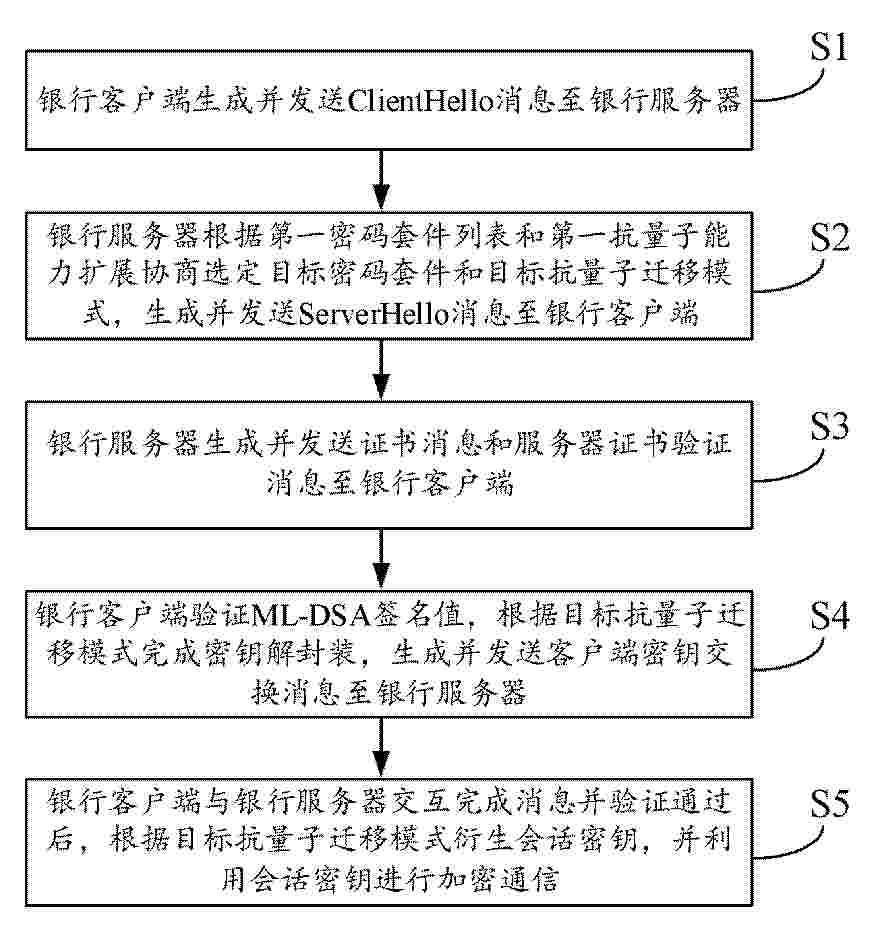
The invention discloses a TLS protocol handshake method and system suitable for the bank industry, and relates to the technical field of quantum cryptography migration resistance, and the method comprises the steps: a bank client generates and sends a ClientHello message to a bank server; the bank server generates a Server Hello message and sends the Server Hello message to the bank client; the bank server generates and sends a certificate message and a server certificate verification message to the bank client; the bank client verifies the ML-DSA signature value, key de-encapsulation is completed according to the target anti-quantum migration mode, and a client key exchange message is generated and sent to the bank server; and after the bank client interacts with the bank server to complete the message and the verification is passed, deriving a session key according to the target anti-quantum migration mode, and carrying out encrypted communication by using the session key. According to the invention, the risk of connection interruption caused by protocol stiffness is effectively avoided, and a stable and reliable anti-quantum migration path is provided for a bank stock network environment.
 BOPI
 Sede Electrónica